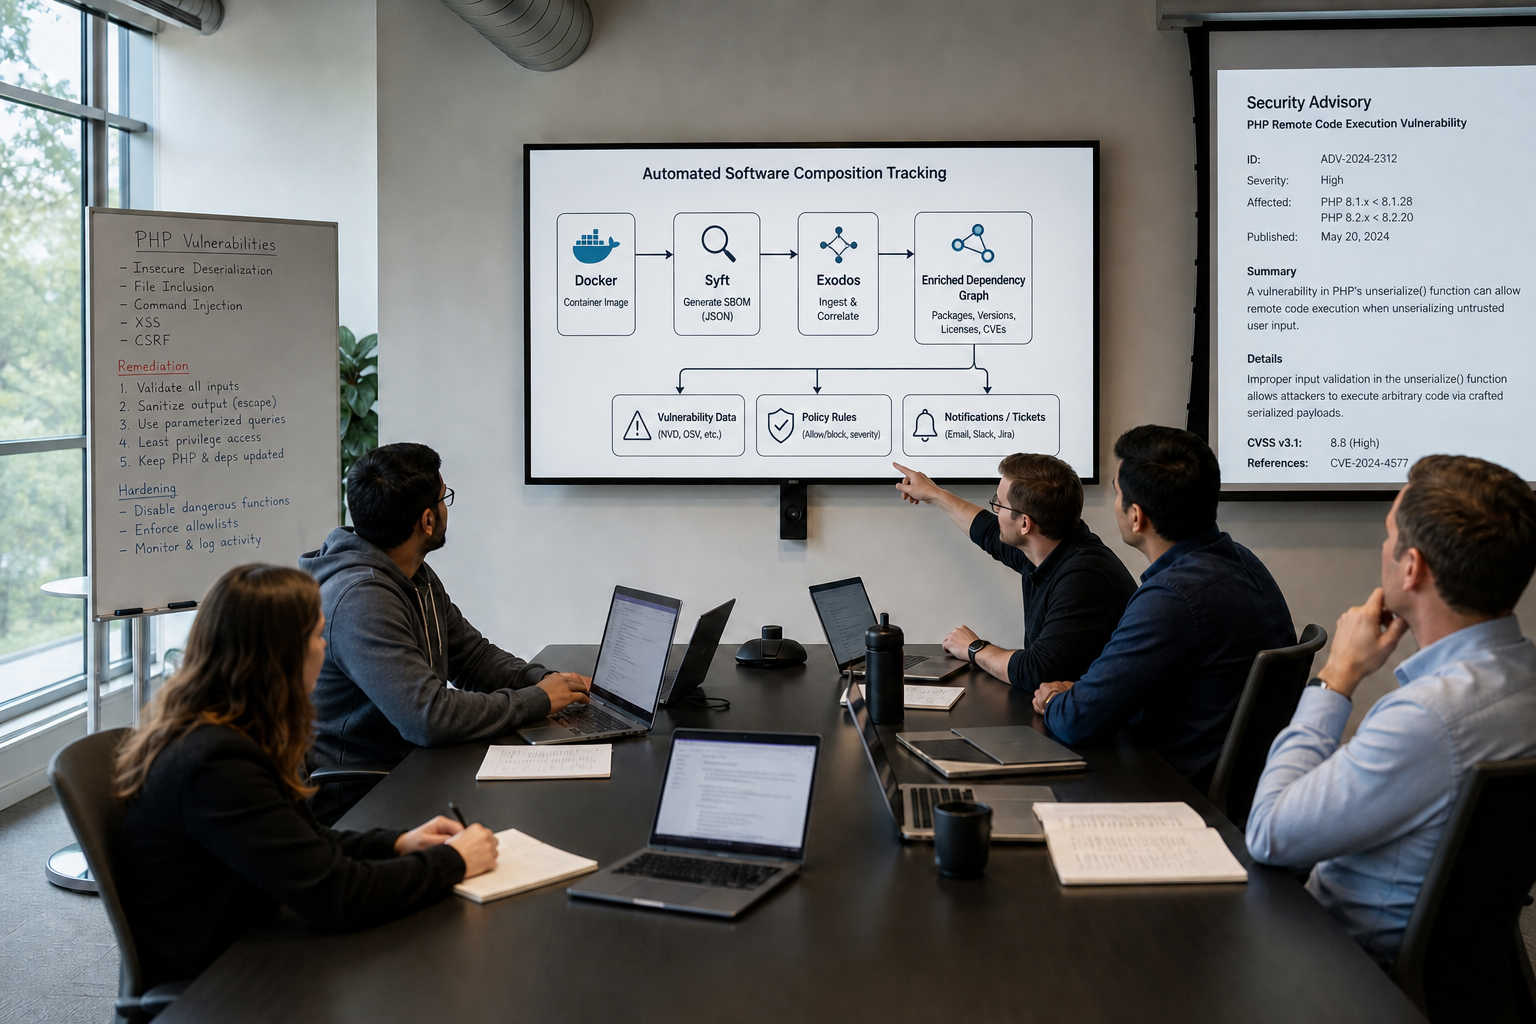
We should already know where PHP is running
Discover how to effectively manage PHP installations and vulnerabilities with automated inventory tracking and SBOM integration for enhanced security.
Read more →
Latest thinking on SBOMs, supply chain security, and the regulations shaping both.
Discover how to effectively manage PHP installations and vulnerabilities with automated inventory tracking and SBOM integration for enhanced security.
Read more →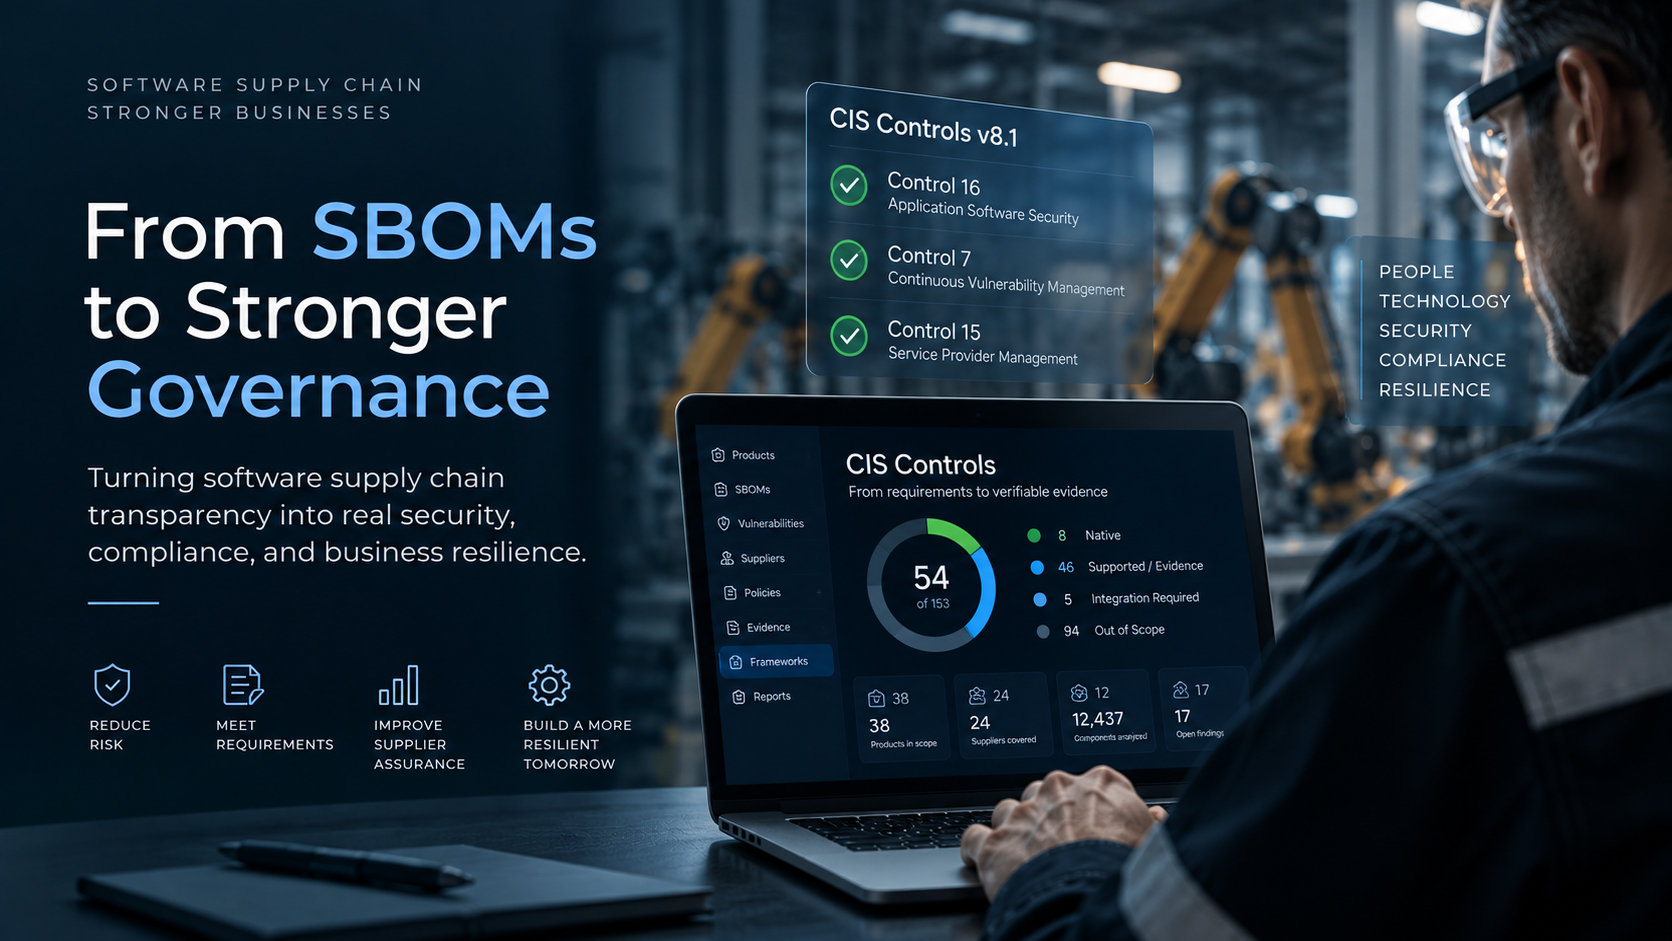
Learn how SBOM management supports key CIS Controls for application security, vulnerability management and continuous software supplier governance.
Read more →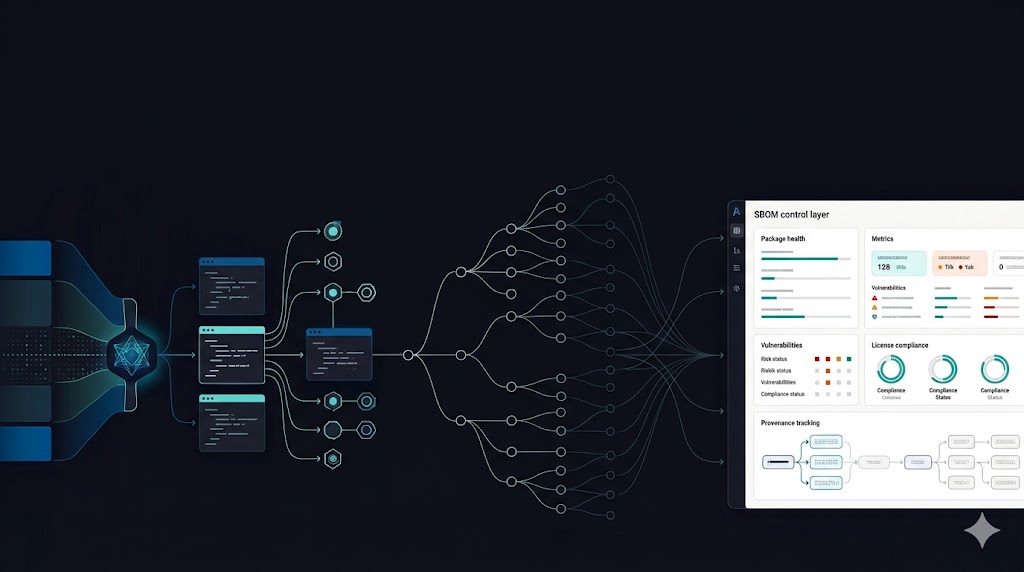
AI coding tools do not eliminate open-source risk. They can accelerate dependency adoption and make SBOM-based governance more important.
Read more →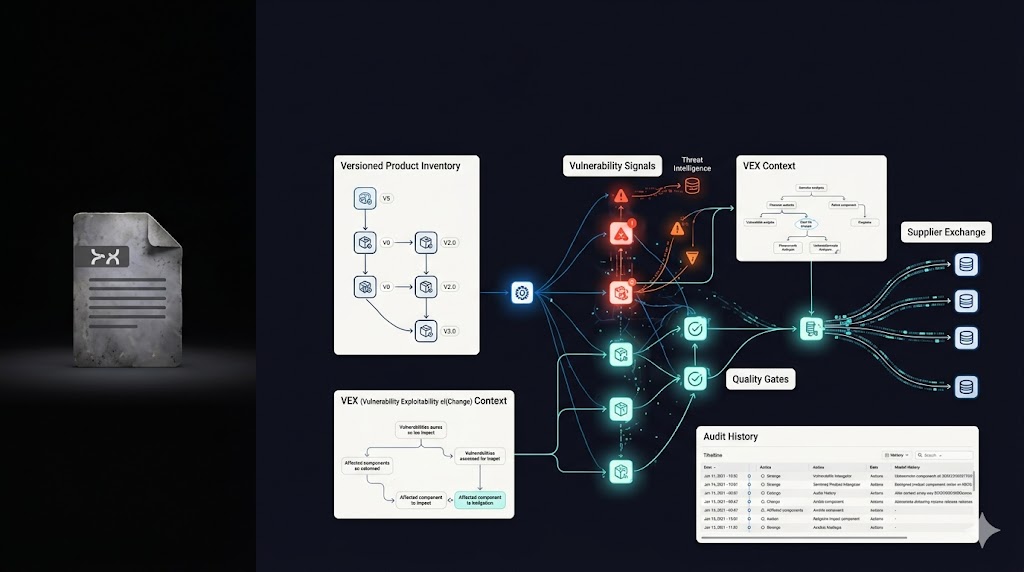
Generating or scanning an SBOM once is not enough. SBOM management requires history, quality gates, vulnerability context, supplier workflows, VEX, an...
Read more →
Many companies still manage open-source license notices with PDFs, static web pages, and manual release work. SBOM-driven FOSS disclosure changes that...
Read more →
The Cyber Resilience Act is often treated as a 2027 deadline. But reporting obligations start on 11 September 2026. Companies need SBOM workflows now.
Read more →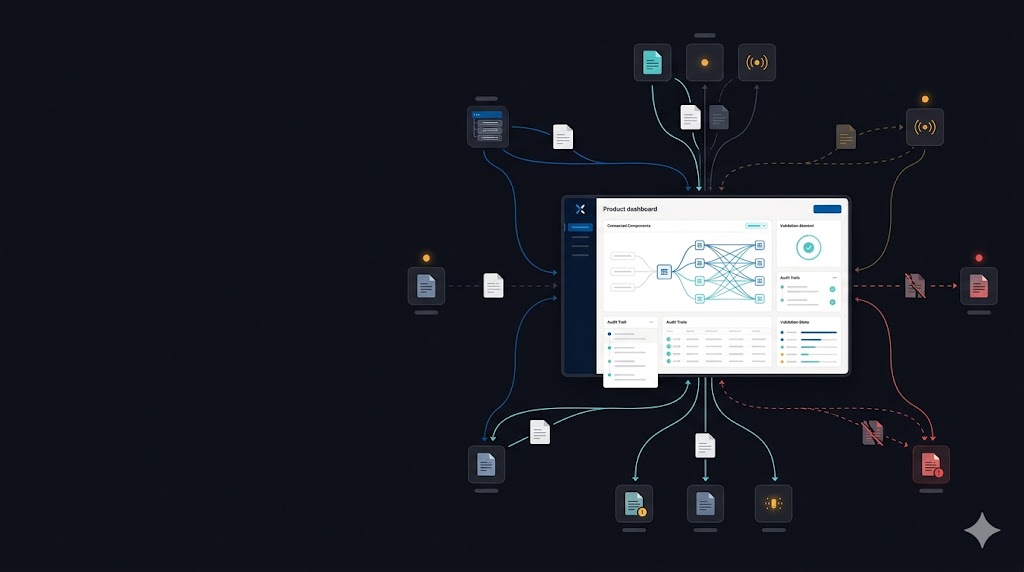
Supplier SBOM management is not a document problem. It is a response, quality, redaction, and incident workflow problem across every vendor you rely o...
Read more →
Secure SBOM sharing without oversharing: public disclosures + controlled access using ABAC, redaction, NDA workflows, and audit trails.
Read more →
Reference CI/CD architecture for SBOMs: generate per build, validate with quality gates, store versioned inventory, and stay audit-ready.
Read more →
Supplier SBOM requests don’t scale via email. Use this kit: templates, SLAs, tracking, and quality gates, to stay audit-ready.
Read more →Analyze an SBOM for free or talk to our team about managing software supply chain data at scale.