Unknown origins
Risk of copyright infringement, PII exposure, or sanctioned source datasets.
Exodos Labs uses advanced AI to analyze, verify, and explain what's inside your software, delivering clarity across SBOMs, provenance, vulnerabilities, and compliance in one secure platform.
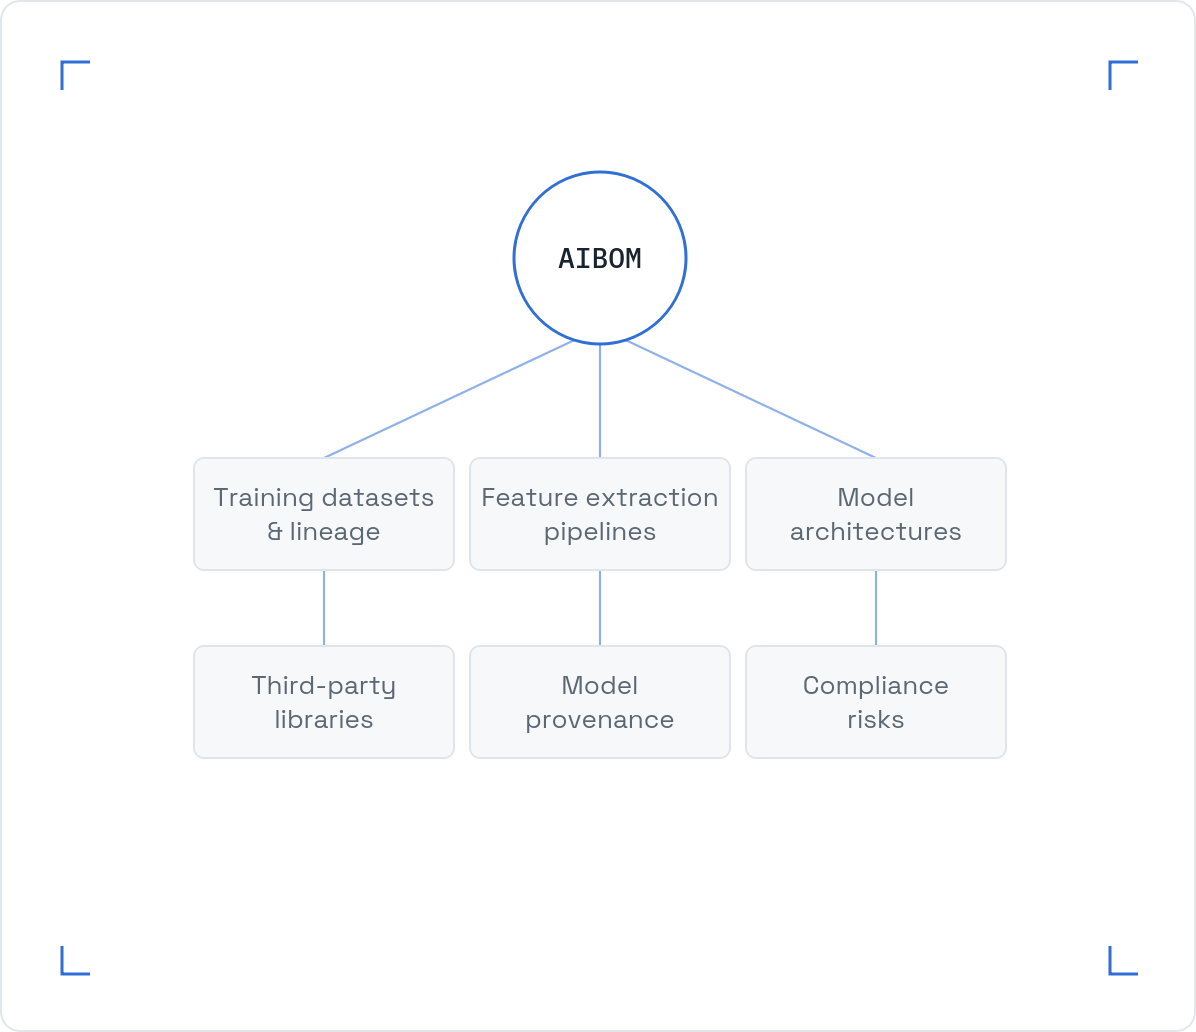
An Artificial Intelligence Bill of Materials (AIBOM) is not a successor to the SBOM, but an expanded lens that adds critical visibility into the models, data, and risks that shape AI-driven systems.
Risk of copyright infringement, PII exposure, or sanctioned source datasets.
LLMs, embeddings, quantized models, and runtimes can carry vulnerabilities or licensing obligations.
AI pipelines change weekly; auditing them manually is unrealistic.
The EU AI Act requires provenance evidence, audit trails, and risk classification.
Automotive, industrial, medical, and financial systems increasingly embed AI models.
No ownership, no lifecycle controls, no continuous assurance once models are deployed.
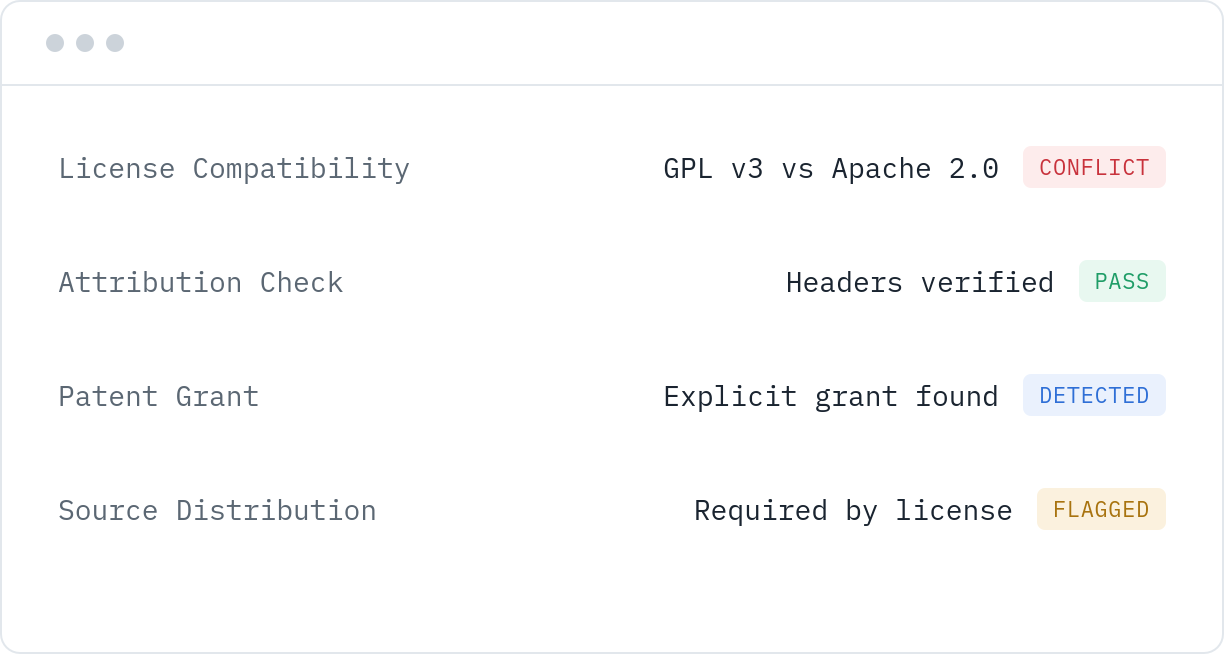
Open source licensing rules are complex and inconsistent. Traditional tools miss subtle conflicts. Our AI reads license texts like a legal engineer to solve complex issues.
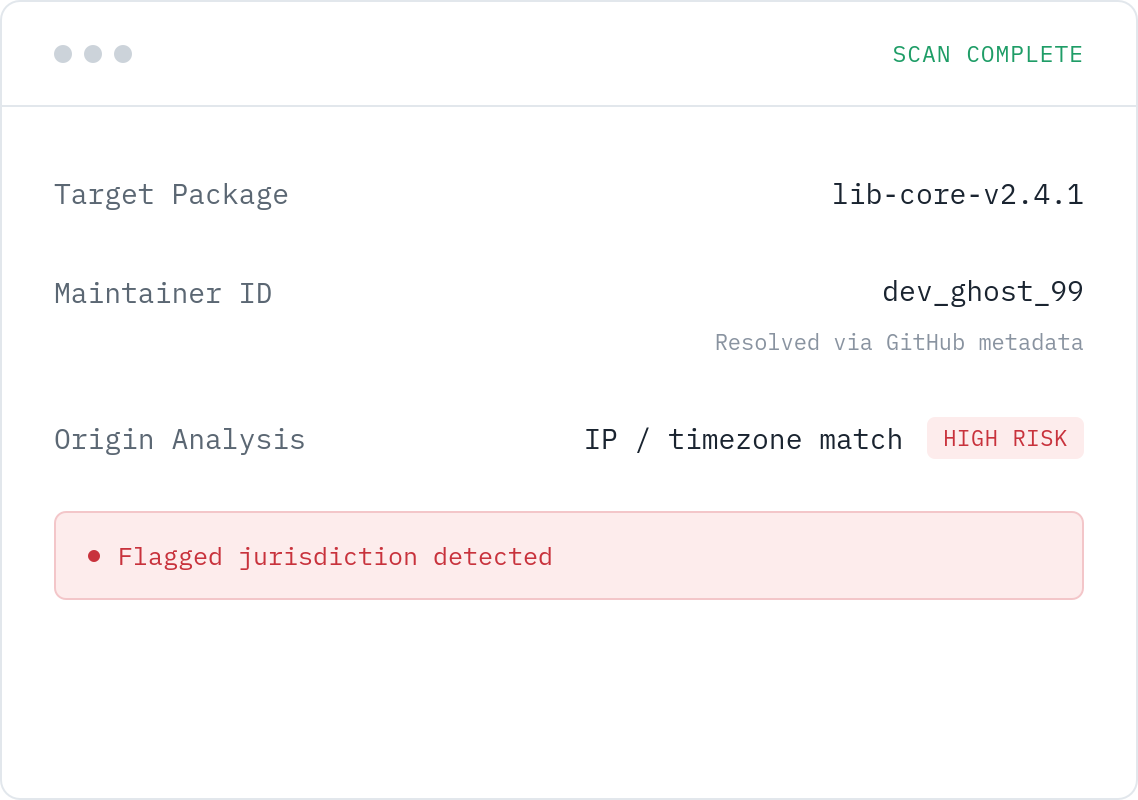
One of the biggest blind spots today: where do your open source components actually come from? Most SBOM tools don't answer who maintains a package or where they're located.
Join security and engineering teams who have transformed their SBOM management from a compliance burden into a strategic advantage.