Release Blockers
Last-minute SBOM requirements delay releases. Manual generation takes hours. Format issues require rework. Compliance becomes a bottleneck you learn to resent.
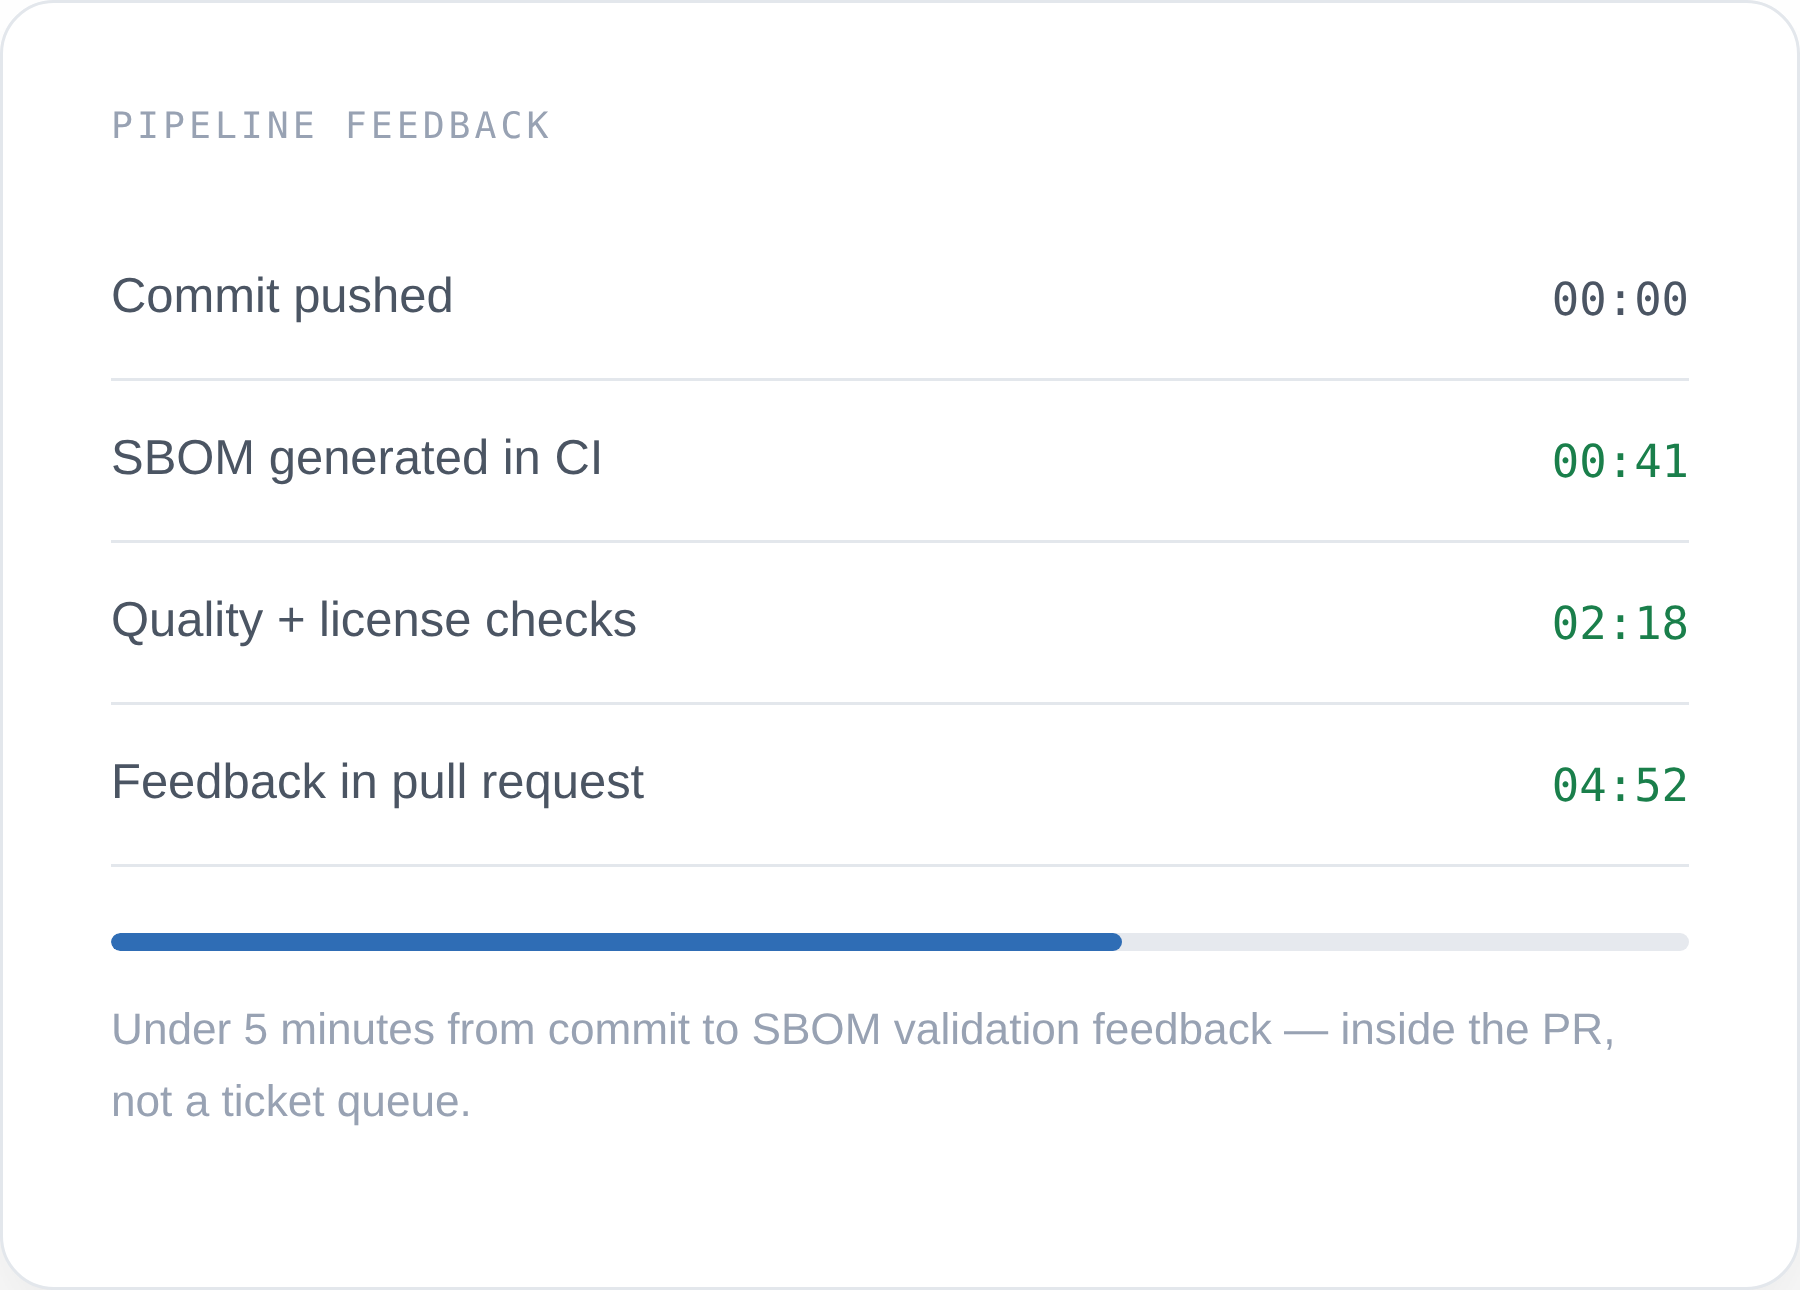
Automated SBOM repository and quality validation that integrates invisibly into your existing CI/CD workflows.
You’re a week from release when compliance asks for updated SBOMs. Again. You generate them manually, send them off, and three days later they’re rejected for “quality issues” you don’t understand. Your velocity suffers. Your team resents compliance. And the cycle repeats next quarter.
Last-minute SBOM requirements delay releases. Manual generation takes hours. Format issues require rework. Compliance becomes a bottleneck you learn to resent.
SBOMs often get generated to satisfy a requirement, but the data is rarely used again until the next audit or incident. When a vulnerability emerges, teams still have to reconstruct product and dependency context manually. Compliance becomes a disconnected step instead of part of the engineering workflow.
Another security tool means another login, another dashboard, another workflow disruption. You already juggle enough tools. Adding one more hurts productivity.
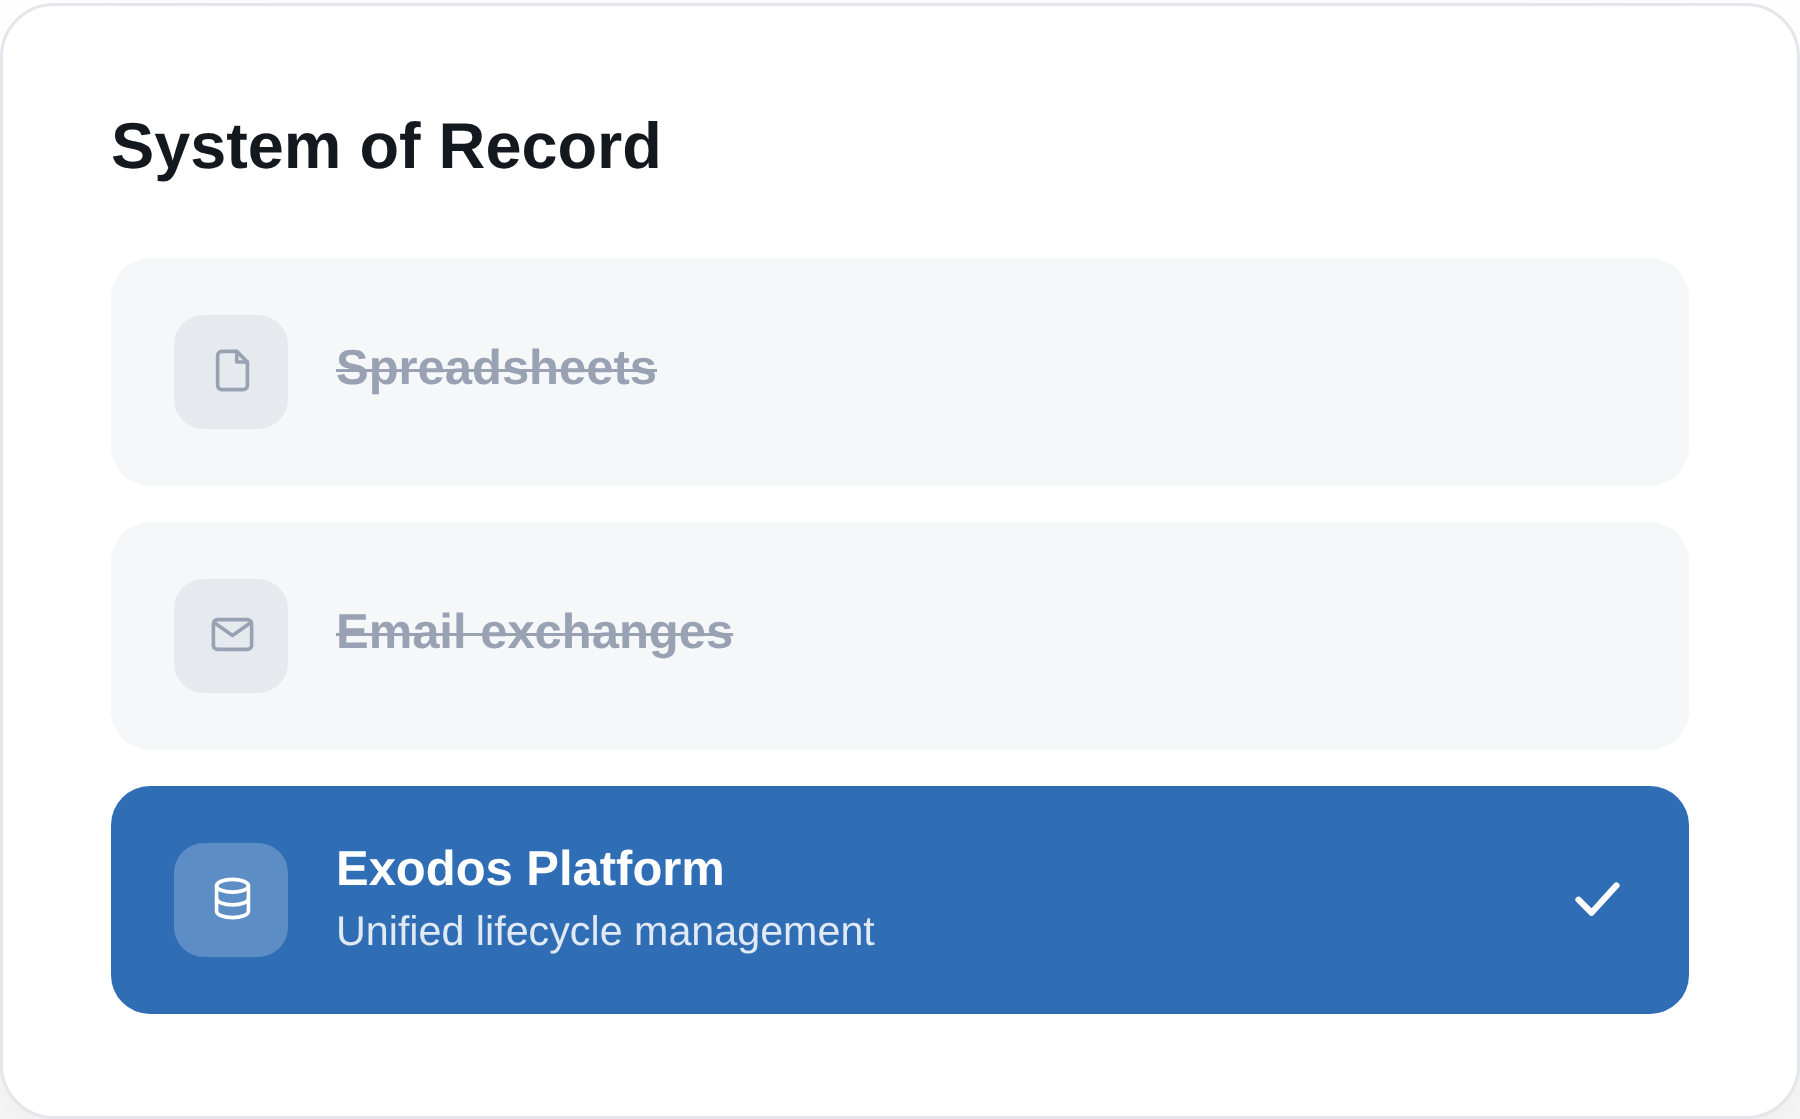
Manage SBOMs end-to-end across their entire lifecycle: from ingestion and validation to versioning, sharing, and ongoing updates. Exodos Labs centralizes all SBOMs in a single, authoritative system of record with full traceability, lifecycle context, and immutable audit trails.
Eliminate fragmentation across tools, teams, and suppliers, and turn SBOMs from static artifacts into operational assets.
Most organizations still handle SBOMs as files: generated once, stored somewhere, and revisited only when auditors or incidents force the issue.
Exodos Labs takes a different approach.
SBOM Operations provides a structured, continuously updated foundation where SBOMs are:
That’s how long it takes to deploy Exodos until you start seeing first results
Last-minute release delays from SBOM issues
Average time from commit to SBOM validation feedback
Developer satisfaction — compliance that doesn’t interrupt flow
SBOMs are continuously ingested from CI/CD pipelines, APIs, and suppliers.
Each SBOM is checked against NTIA and custom organizational policies on arrival.
Changes are recorded against builds, releases, and products with full lifecycle context.
Component state and decisions are maintained across versions and releases.
SBOM Operations & Lifecycle Management is used by:
SBOMs are no longer optional, but operational excellence with SBOMs is still rare.
Exodos Labs gives organizations a practical, scalable way to manage SBOMs as living assets, enabling security, compliance, and transparency without friction.
Join security and engineering teams who have transformed their SBOM management from a compliance burden into a strategic advantage.