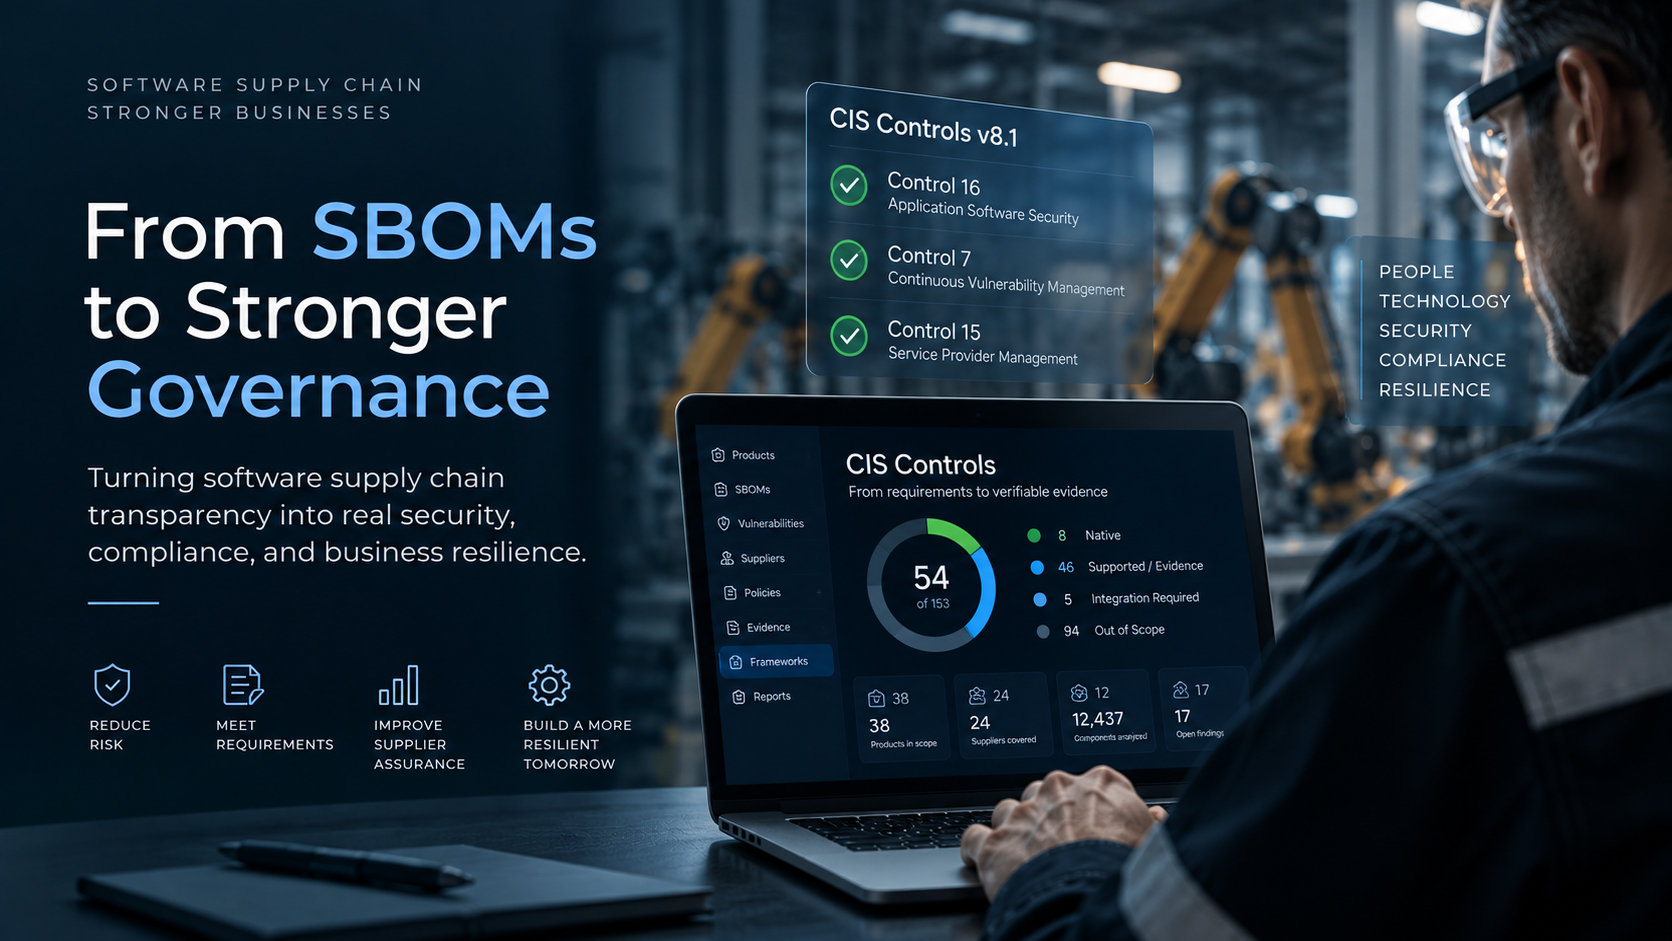
Your SBOM Program May Already Be a CIS Controls Program
Learn how SBOM management supports key CIS Controls for application security, vulnerability management and continuous software supplier governance.
Read more →
Latest thinking on SBOMs, supply chain security, and the regulations shaping both.
Learn how SBOM management supports key CIS Controls for application security, vulnerability management and continuous software supplier governance.
Read more →
Many companies still manage open-source license notices with PDFs, static web pages, and manual release work. SBOM-driven FOSS disclosure changes that...
Read more →
The Cyber Resilience Act is often treated as a 2027 deadline. But reporting obligations start on 11 September 2026. Companies need SBOM workflows now.
Read more →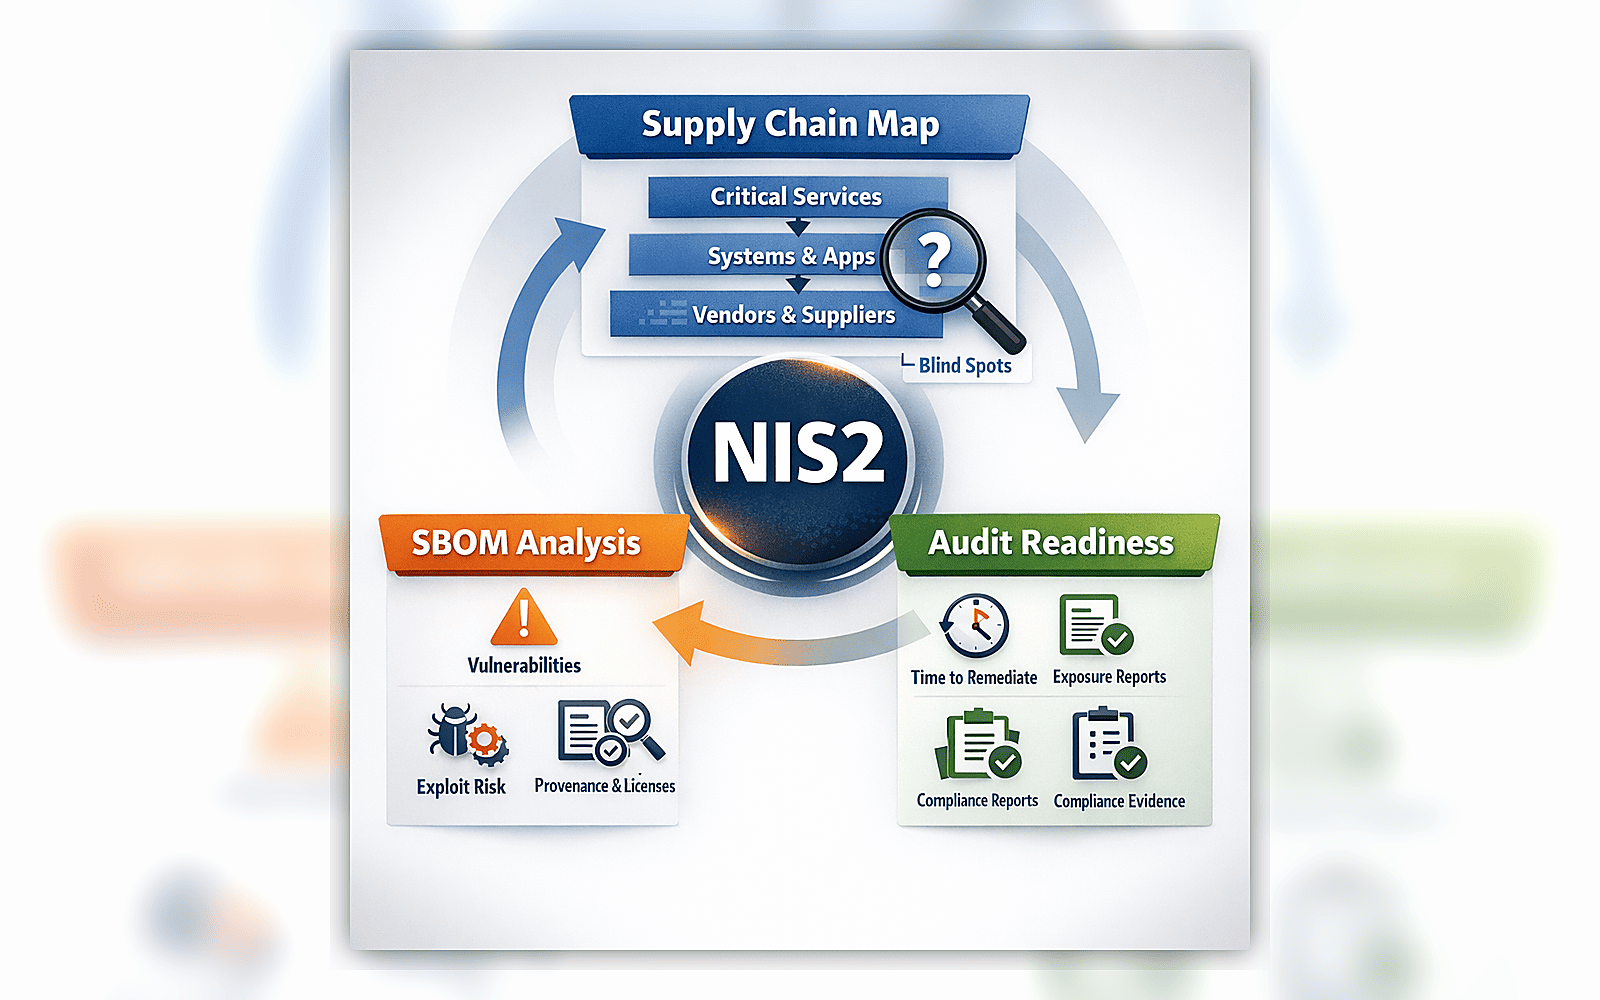
Practical steps for EU essential and important entities to map software supply chain risk, operationalize SBOMs, and prepare for NIS2 audits.
Read more →
Learn why SBOMs are essential for true Sovereign Cloud compliance and how they provide the crucial evidence layer for software supply chain security.
Read more →
Explore how the OpenChain AI SBOM Framework strengthens AI governance—closing operational gaps and turning principles into actionable, auditable contr...
Read more →
Golden images must evolve continuously. Learn why static baselines fail and how a living golden image strengthens security and compliance.
Read more →
The EU Cyber Resilience Act is coming. Learn how software vendors can prepare for CRA compliance with a practical, step-by-step readiness playbook.
Read more →
DORA, NIS2, and the EU CRA raise the bar for software supply chain security. Learn how SBOMs become mandatory for compliance and risk control.
Read more →
Regulators demand continuous FOSS compliance. Learn why static PDFs fail and how AI-driven automation delivers audit-ready, scalable compliance.
Read more →Analyze an SBOM for free or talk to our team about managing software supply chain data at scale.