Built on Open Source. Secured for Everyone.
We support open source projects and teams with free access to enterprise-grade SBOM and software supply chain tooling.
Why We Invest in the Community
Modern software is built on open source, but securing it is still too hard.
Software supply chains are complex, distributed, and often lack visibility. That creates risk for everyone, from individual developers to global enterprises.
We believe security shouldn’t be limited to those who can afford it.
That’s why we actively support open source projects and community-driven teams with access to the same tools used by enterprise organizations.
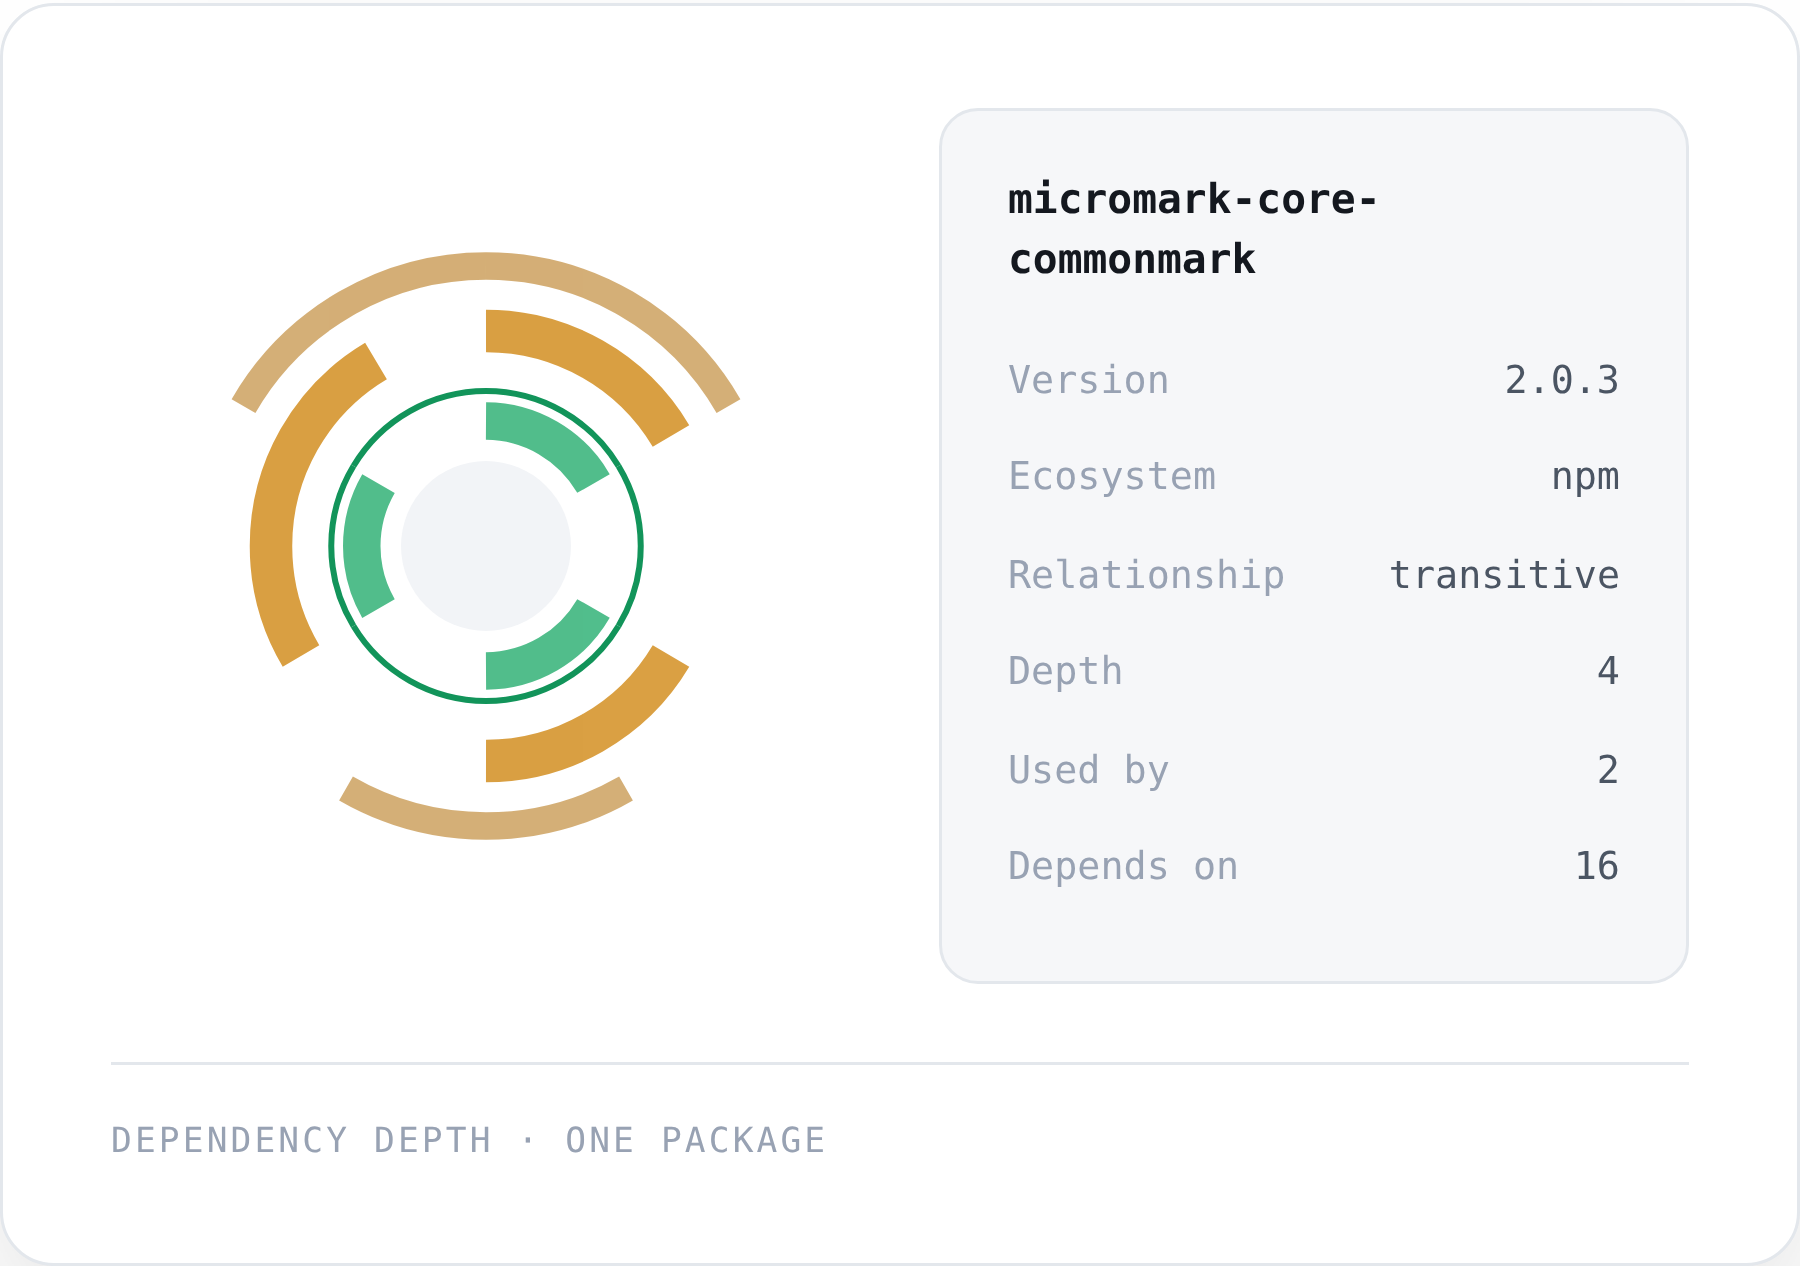
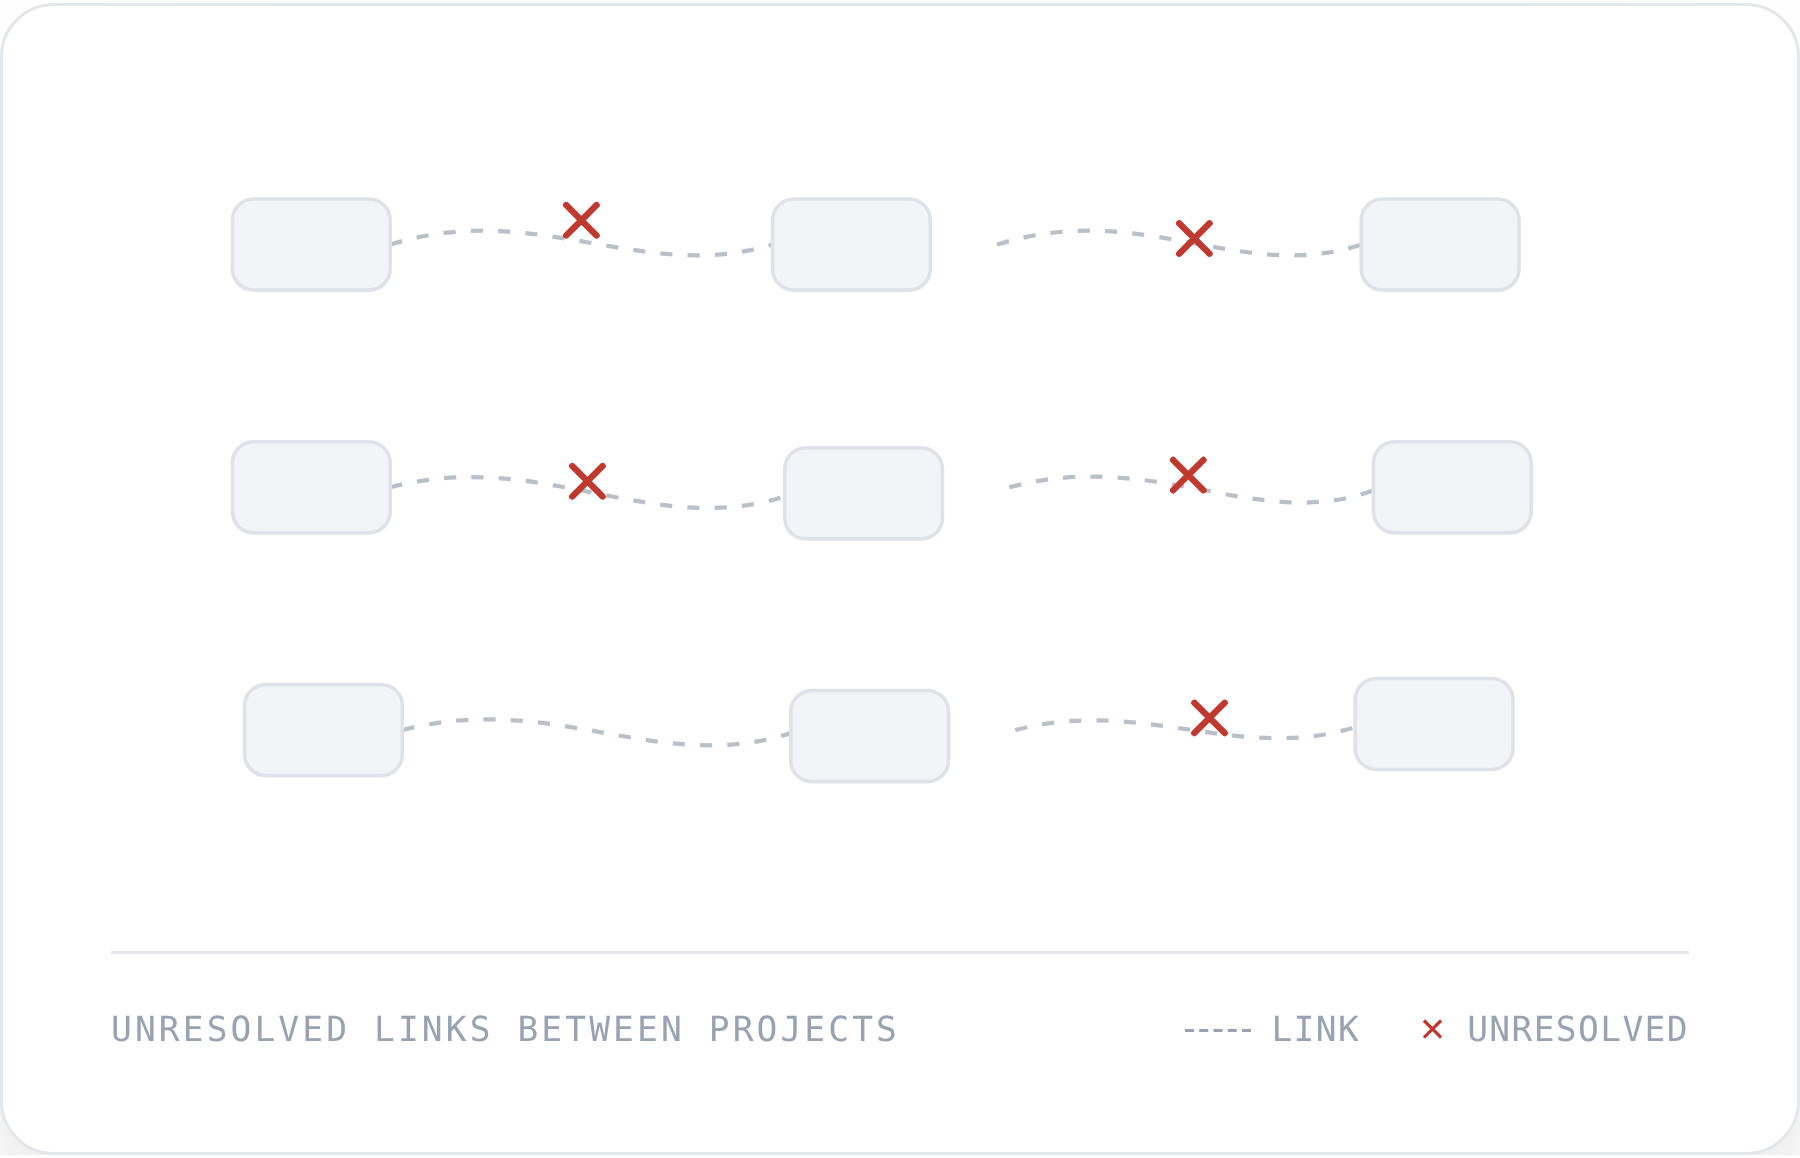
Open source powers today’s software, but also introduces:
- Unknown dependencies across projects
- Limited visibility into vulnerabilities
- Manual and fragmented SBOM management
- Increasing compliance pressure (e.g. EU CRA)
Without proper tooling, even experienced teams struggle to understand and secure their own supply chain.
One system of record for real-world workflows
We provide a centralized platform to:
- Generate and manage SBOMs
- Identify vulnerabilities and license risks
- Track dependencies across projects
- Securely share SBOM data with collaborators
All in one system of record designed for real-world workflows, not spreadsheets and emails.
See the Architecture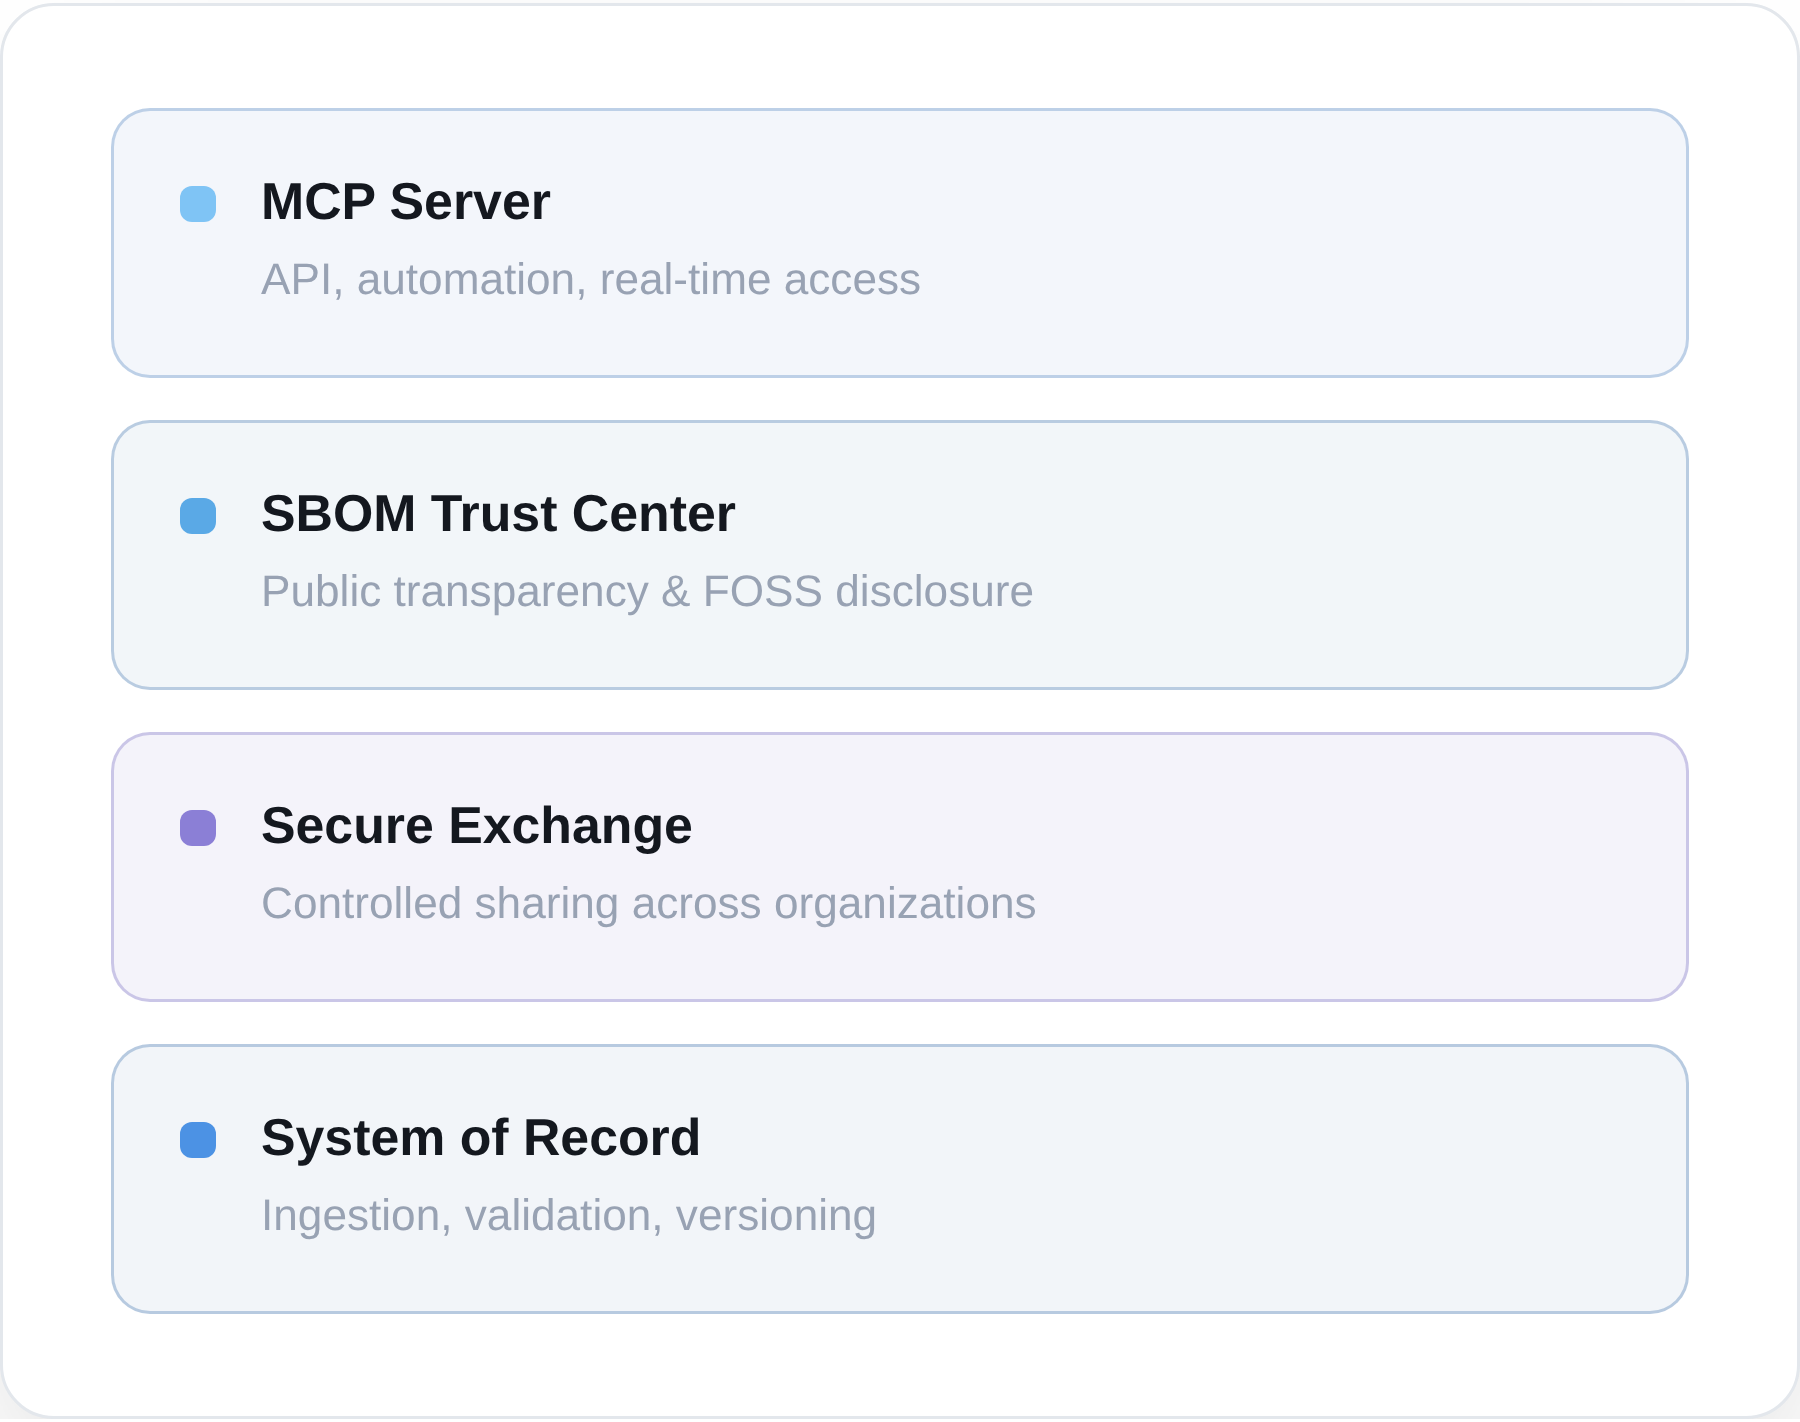
Apply for Access
This program is designed for:
- Open source maintainers and core teams
- Security and infrastructure projects
- Developer tooling ecosystems
- Research and non-commercial initiatives
If your work improves software security, transparency, or reliability, we want to support it.
3 Simple Steps
If your work improves software security, transparency, or reliability, we want to support it.
Structured SBOM workflows
Generate, ingest, and manage SBOMs in a consistent workflow from development to release - without manual overhead.
Version-aware tracking
Maintain a complete history of your software components and track changes across builds, releases, and environments.
Not ready to apply?
You can start using our free tools immediately:
- Free SBOM Scan
- Free CRA Readiness Check
- Free SBOM Management
Instant vulnerability insights
Upload an SBOM and immediately identify known vulnerabilities and affected components.
Compliance without complexity
Check readiness, validate requirements, and generate reports without setting up complex tooling.
Transparency Starts With Us
We believe software transparency should be continuous, accessible, and operational, not hidden behind PDFs, spreadsheets, or disconnected compliance processes.
That’s why we publicly publish parts of our own software inventory and FOSS disclosures through the Exodos Labs Trust Center.
Using the same platform and workflows we provide to customers, our Trust Center continuously publishes selected software supply chain information directly from our CI/CD-driven SBOM processes.
This enables customers, partners, and the broader community to:
- Understand which open source components we use
- Review licenses and software inventory information
- Access continuously updated disclosures
- Experience how operational software transparency can work in practice
For us, this is not just a compliance exercise. It’s part of building trust in modern software supply chains.
Explore our Live Trust Center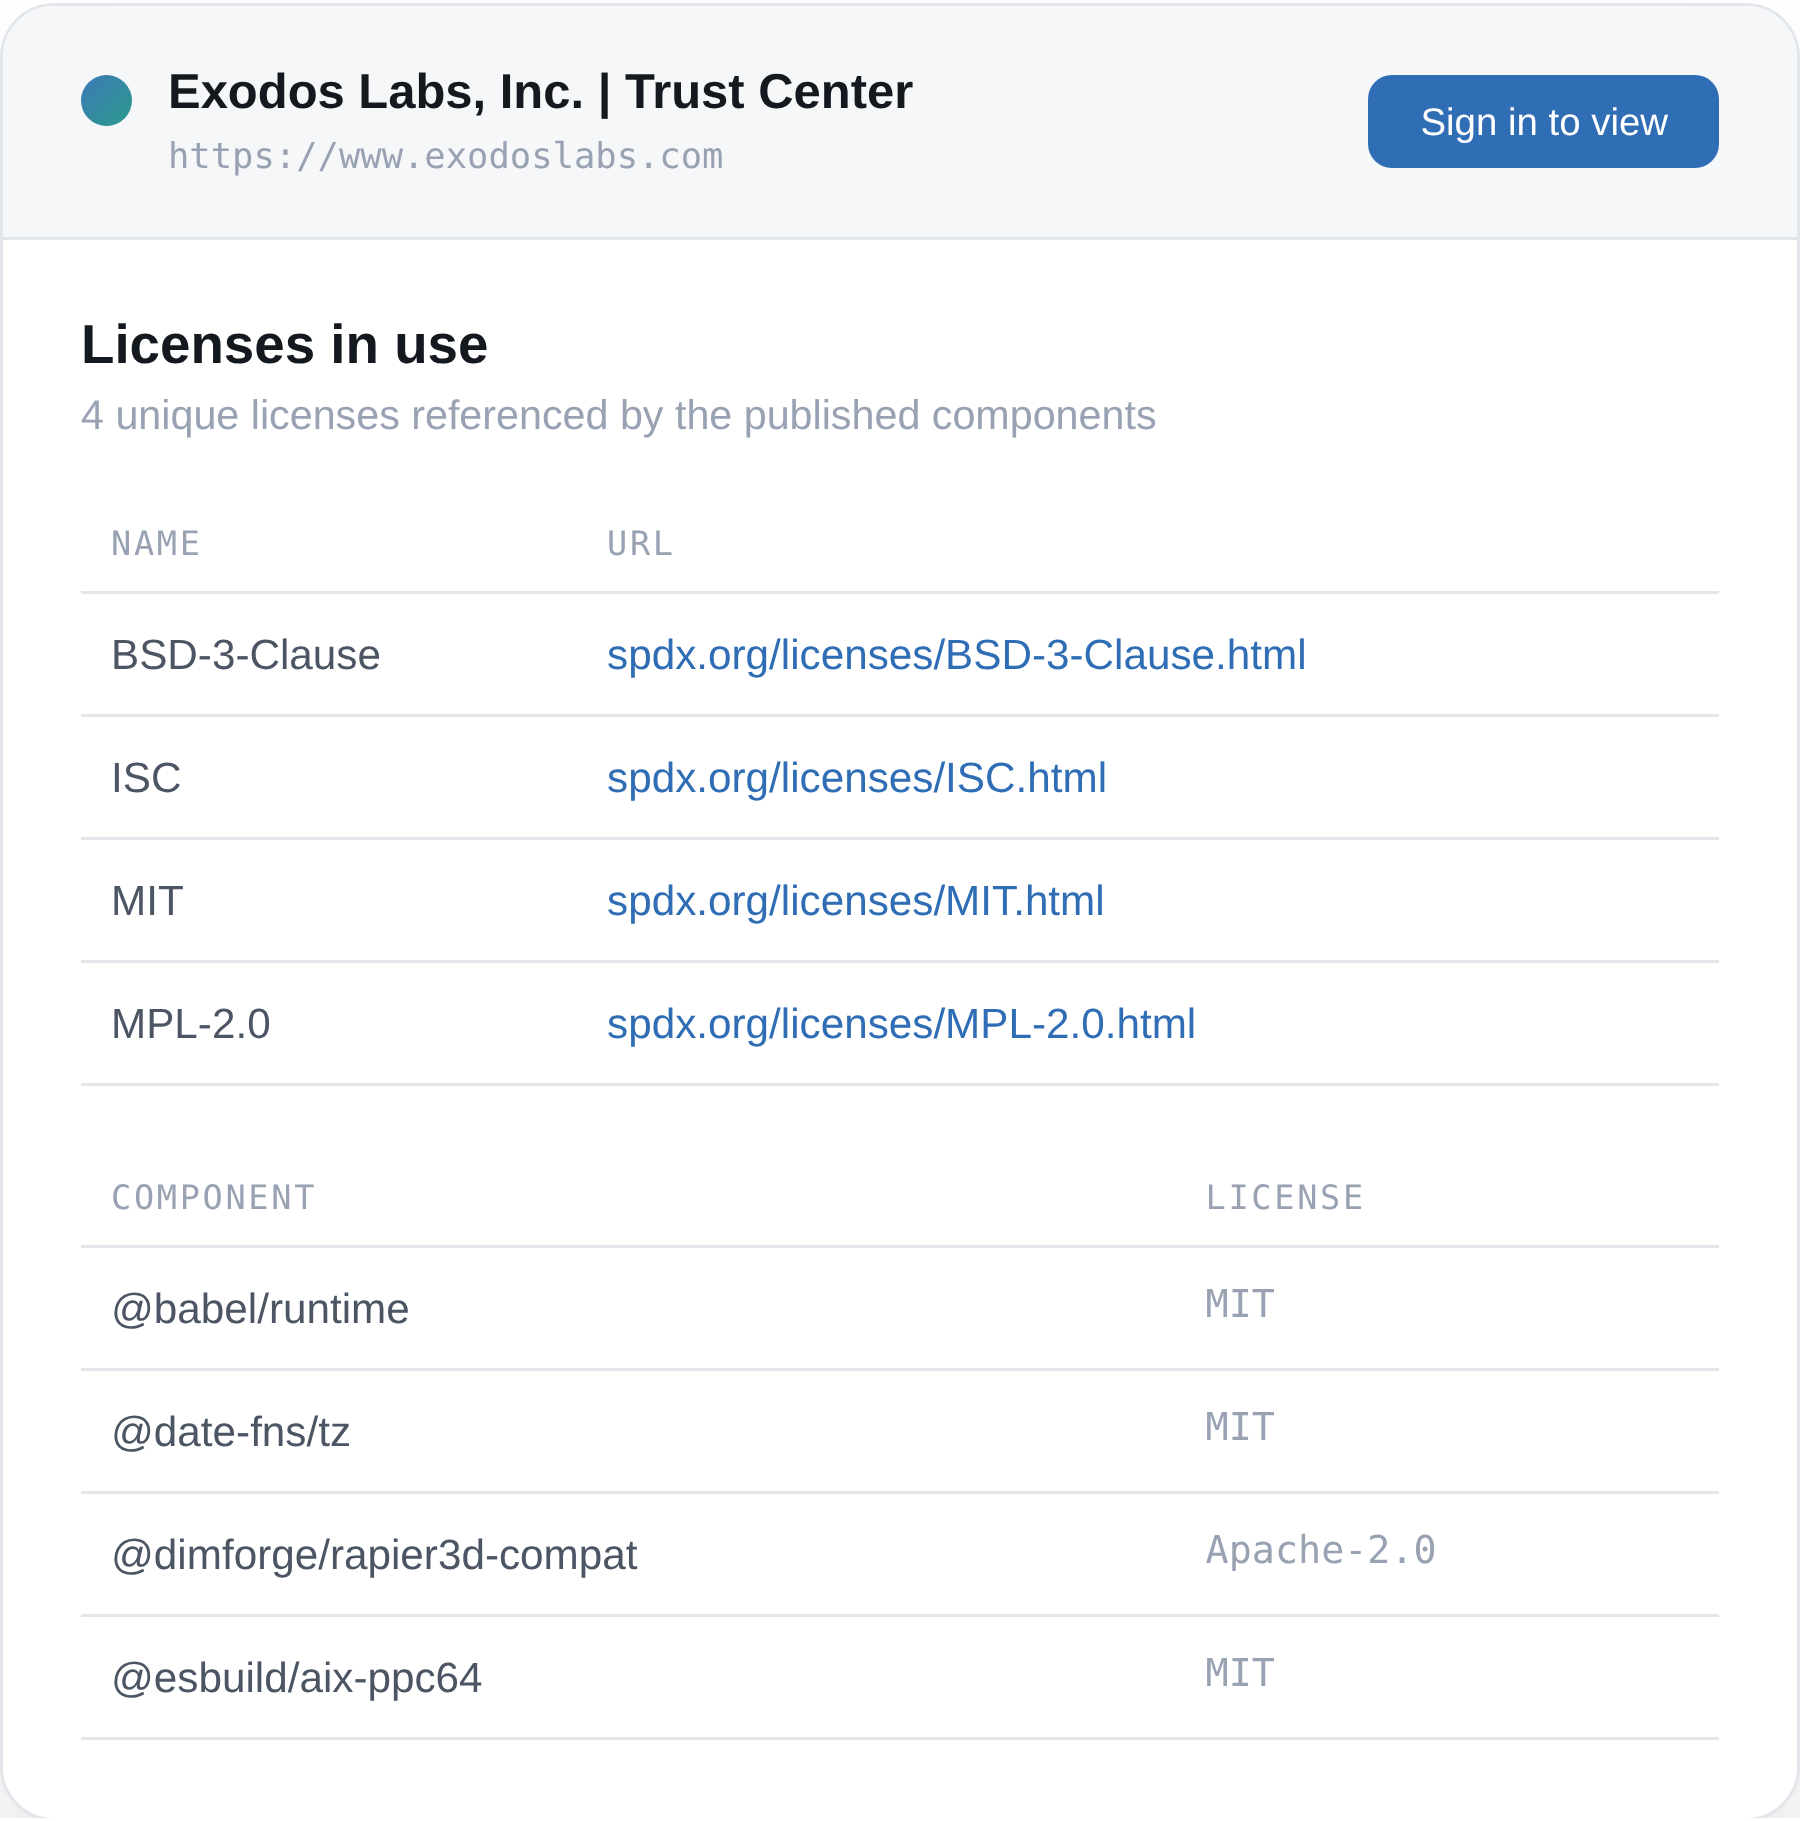
Start Your 14-Day Free Trial Today
Join security and engineering teams who have transformed their SBOM management from a compliance burden into a strategic advantage.