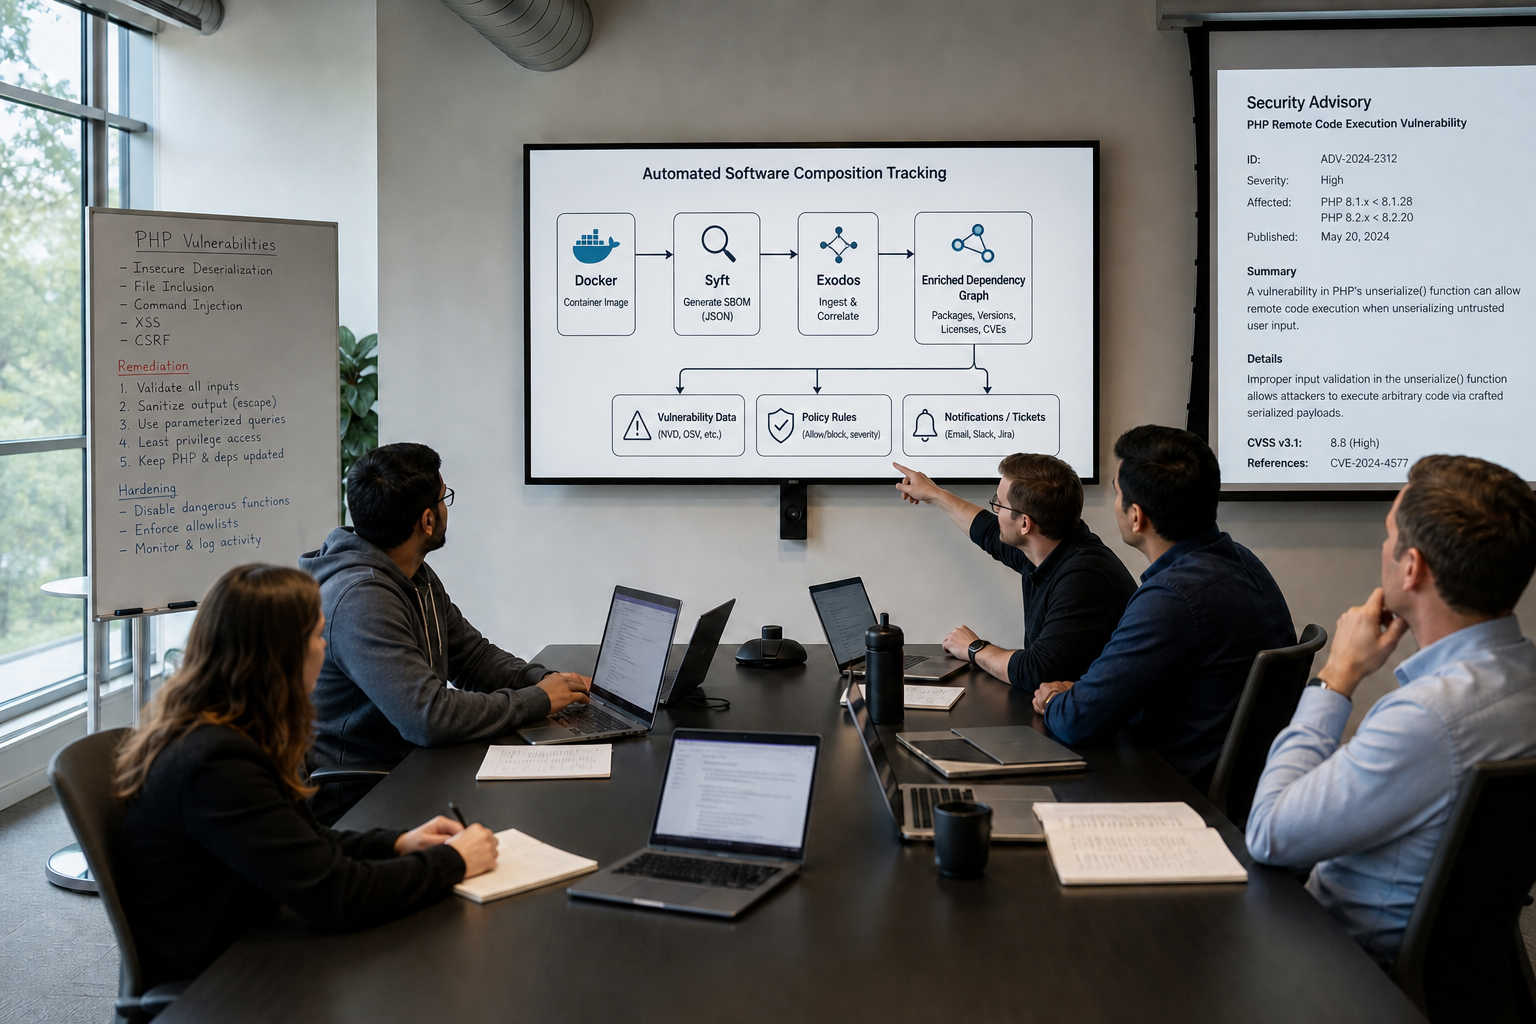
We should already know where PHP is running
Discover how to effectively manage PHP installations and vulnerabilities with automated inventory tracking and SBOM integration for enhanced security.
Read more →
Latest thinking on SBOMs, supply chain security, and the regulations shaping both.
Discover how to effectively manage PHP installations and vulnerabilities with automated inventory tracking and SBOM integration for enhanced security.
Read more →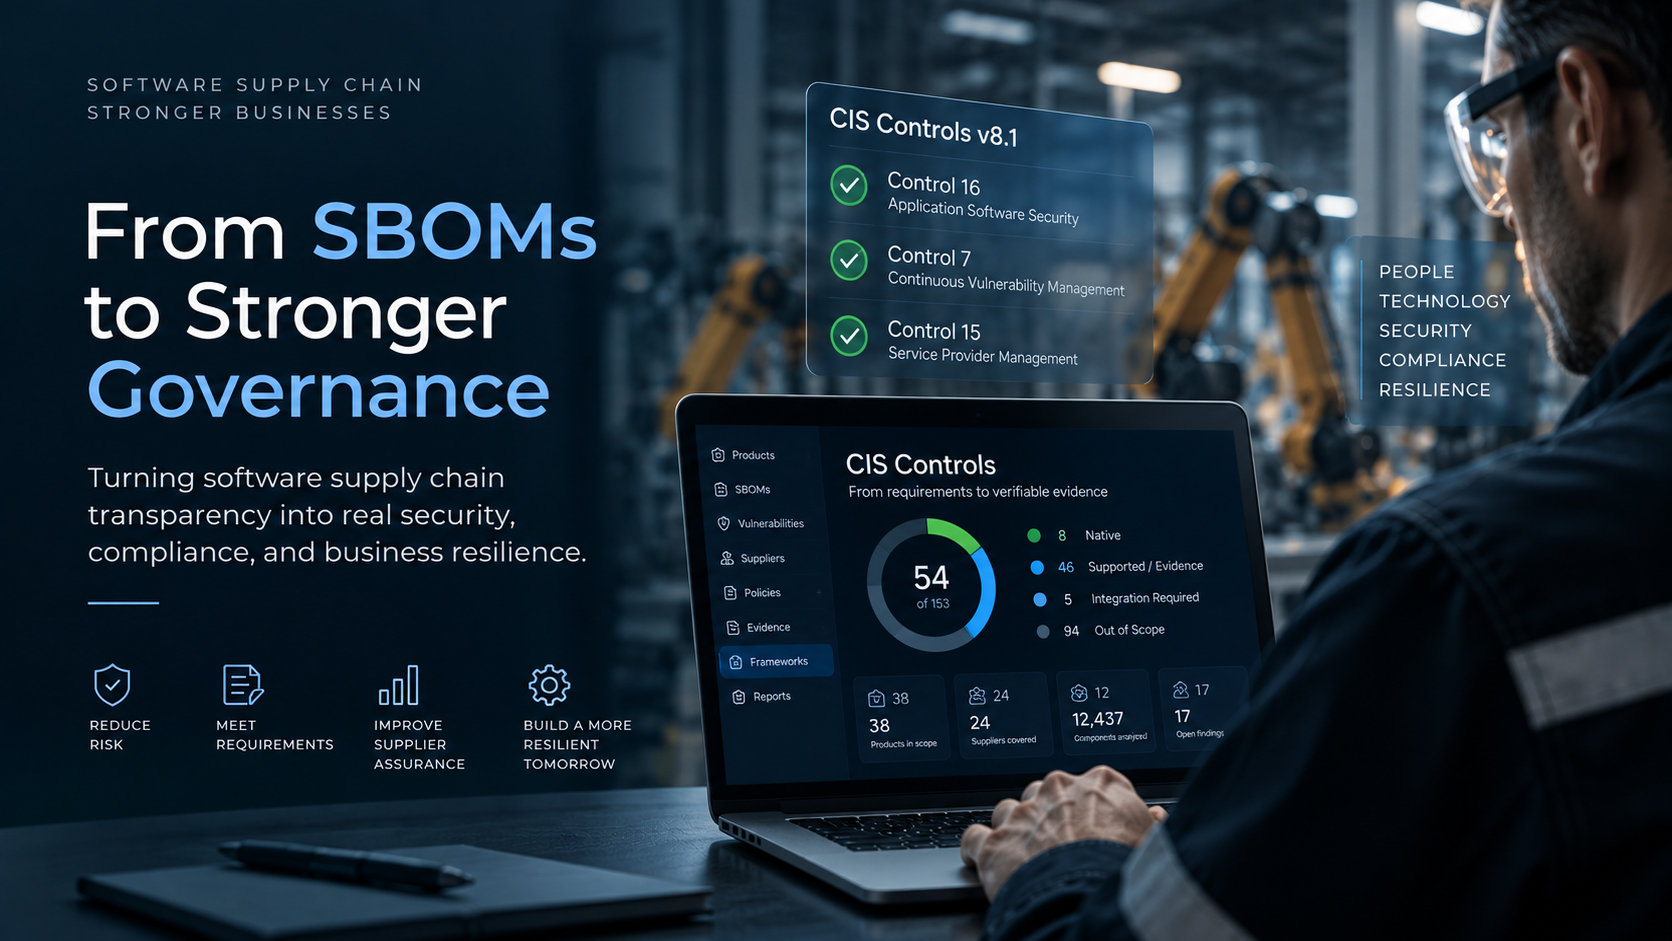
Learn how SBOM management supports key CIS Controls for application security, vulnerability management and continuous software supplier governance.
Read more →
Secure SBOM sharing without oversharing: public disclosures + controlled access using ABAC, redaction, NDA workflows, and audit trails.
Read more →
Supplier SBOM requests don’t scale via email. Use this kit: templates, SLAs, tracking, and quality gates, to stay audit-ready.
Read more →
NTIA minimum SBOM elements aren’t enough. Learn practical SBOM acceptance criteria and quality gates to make SBOMs actionable and auditable.
Read more →
Learn why SBOMs are essential for true Sovereign Cloud compliance and how they provide the crucial evidence layer for software supply chain security.
Read more →
Golden images must evolve continuously. Learn why static baselines fail and how a living golden image strengthens security and compliance.
Read more →
The EU Cyber Resilience Act is coming. Learn how software vendors can prepare for CRA compliance with a practical, step-by-step readiness playbook.
Read more →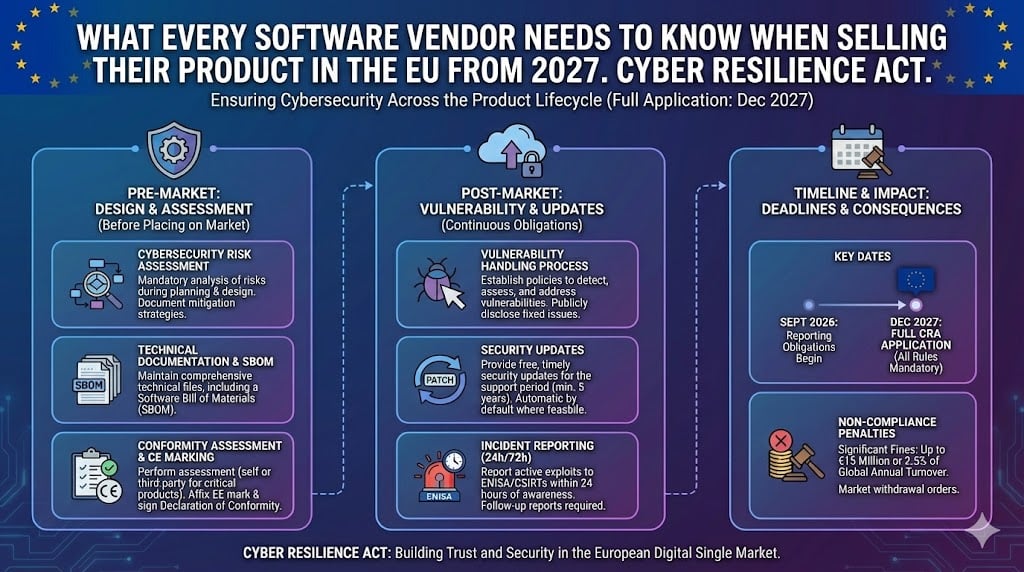
DORA, NIS2, and the EU CRA raise the bar for software supply chain security. Learn how SBOMs become mandatory for compliance and risk control.
Read more →
EU’s quantum alarm is accelerating post-quantum cryptography. Learn how PQC, SBOMs, and CBOMs help organizations prepare for quantum risk.
Read more →Analyze an SBOM for free or talk to our team about managing software supply chain data at scale.