Compare Platforms

See how Exodos Labs compares

Scanners, SCA tools, and SBOM inventories all solve different slices of the problem. Use these side-by-side breakdowns to understand the strengths, trade-offs, and best use cases of leading software supply chain security platforms.

Compare software supply chain platforms

Which software supply chain platform category fits your needs?

Not every tool in the software supply chain ecosystem solves the same problem. Some platforms help developers find vulnerabilities. Others generate SBOMs, analyze licenses, or manage open source risk. Exodos Labs focuses on operationalizing software transparency across teams, suppliers, customers, regulators, and AI systems.

01

Software Composition Analysis

Best for discovering what is inside your software.

SCA tools help organizations identify open source components, known vulnerabilities, and license obligations inside applications.

Typical tools Black Duck, Snyk, JFrog Xray
Best fit
  • Vulnerability discovery
  • License scanning
  • Open source governance
  • Developer security workflows
02

Developer-First Security Scanning

Best for fast CI/CD and container security checks.

Developer-first scanners help engineering teams identify vulnerabilities, misconfigurations, and security issues during development and build workflows.

Typical tools Trivy, Grype, GitHub Advanced Security
Best fit
  • CI/CD security
  • Container scanning
  • Infrastructure-as-code checks
  • Fast developer feedback
03

Open Source SBOM Management

Best for basic SBOM inventory and vulnerability visibility.

Open source SBOM tools help teams store, inspect, and analyze SBOMs, often as a starting point for software transparency initiatives.

Typical tools Dependency-Track
Best fit
  • SBOM inventory
  • Vulnerability visibility
  • Open source deployments
  • Technical experimentation
04

SBOM Visibility Platforms

Best for viewing and managing software transparency artifacts.

SBOM visibility platforms help organizations collect and analyze SBOMs, track software composition, and maintain a searchable record across products.

Typical tools Varies by vendor
Best fit
  • SBOM cataloging
  • Cross-team visibility
  • Basic reporting
05 Exodos Labs Category

Software Supply Chain Intelligence

Best for understanding risk across components, suppliers, maintainers, and ecosystems.

Supply chain intelligence platforms connect component data to supplier relationships, maintainer behavior, provenance, and geopolitical risk — not just what's in the code.

Best fit
  • Supplier & maintainer risk
  • Provenance intelligence
  • Geo-risk analysis
06 Exodos Labs Category

Enterprise SBOM Governance

Best for operationalizing SBOMs across the enterprise.

Enterprise SBOM governance focuses on the full lifecycle of SBOMs: ingestion, validation, quality gates, secure exchange, and audit-ready evidence.

Best fit
  • SBOM lifecycle & quality gates
  • Secure exchange & trust centers
  • Regulatory evidence
Head-to-head comparisons

Compare Exodos Labs against specific tools

Exodos Labs vs Black Duck

Software Composition Analysis

Compare traditional SCA with enterprise SBOM governance and software supply chain intelligence.

  • SBOM governance
  • Vulnerability and license analysis
  • Binary analysis vs SBOM operations
  • Supplier and compliance workflows
Compare Exodos Labs vs Black Duck →

Exodos Labs vs Dependency-Track

Open Source SBOM Management

Compare open-source SBOM visibility with enterprise-grade SBOM operations, exchange, and compliance automation.

  • Open-source SBOM management
  • Enterprise governance
  • Supplier workflows
  • Trust Center publishing
Compare Exodos Labs vs Dependency-Track →

Exodos Labs vs Trivy

Developer-First Security Scanner

Compare CI/CD scanning with continuous SBOM lifecycle management and enterprise software transparency.

  • Vulnerability scanning
  • CI/CD security
  • SBOM generation and analysis
  • Compliance reporting
Compare Exodos Labs vs Trivy →

Exodos Labs vs Snyk

Developer Security

Compare developer-first AppSec with operational software supply chain governance.

  • Open source security
  • Developer workflows
  • SBOM lifecycle management
  • Regulatory readiness
Compare Exodos Labs vs Snyk →

Exodos Labs vs SonarQube

Code Quality and Application Security

Compare developer-first code quality and application security analysis with enterprise SBOM governance and software supply chain operations.

  • Code quality and security analysis
  • SAST, SCA, secrets, and IaC scanning
  • CI/CD quality gates
  • SBOM governance and supplier transparency
Compare Exodos Labs vs SonarQube →
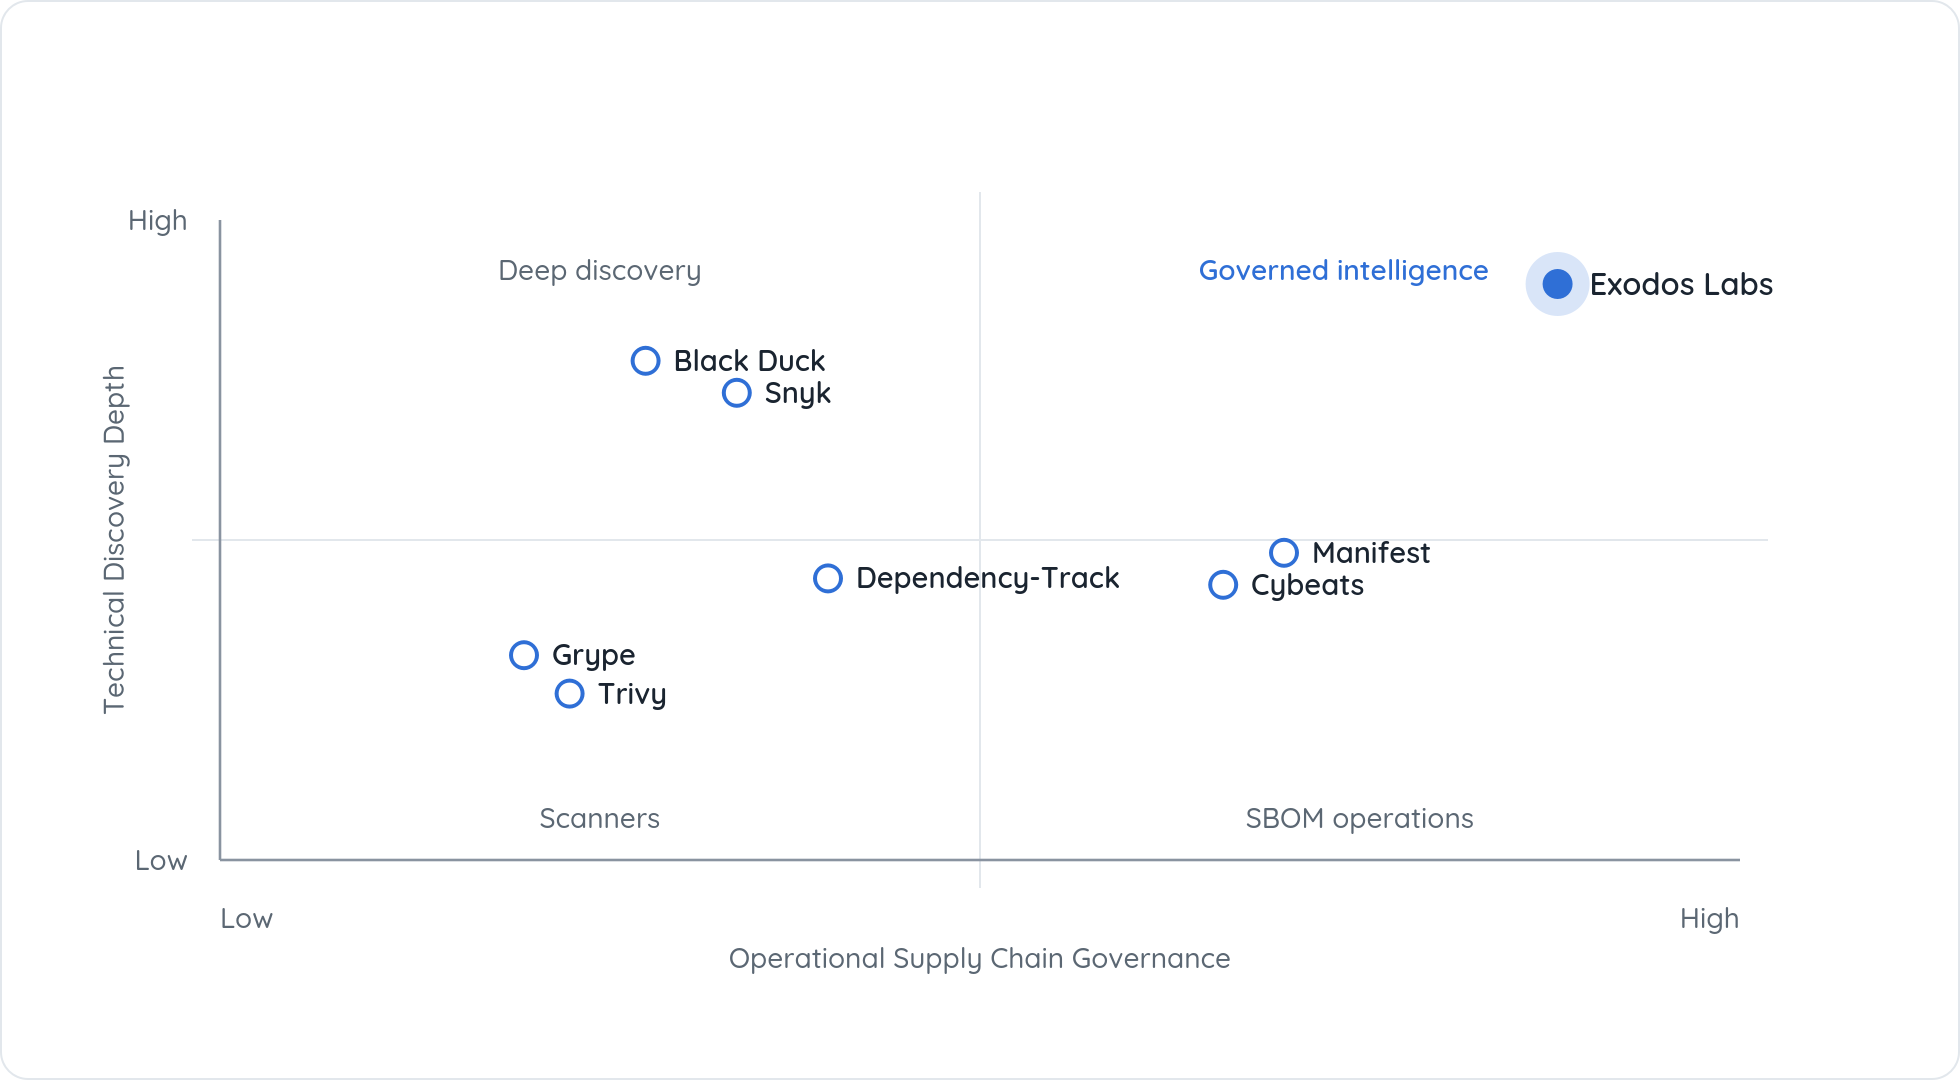
Market positioning

Software supply chain platforms by discovery depth and governance maturity

Looks like Gartner, but it's from us. View how scanner-first, SBOM management, artifact analysis, and governance platforms differ.

Software supply chain platforms by discovery depth and governance maturity
Free Trial

Start Your 14-Day Free Trial Today

Join security and engineering teams who have transformed their SBOM management from a compliance burden into a strategic advantage.